For youLocal
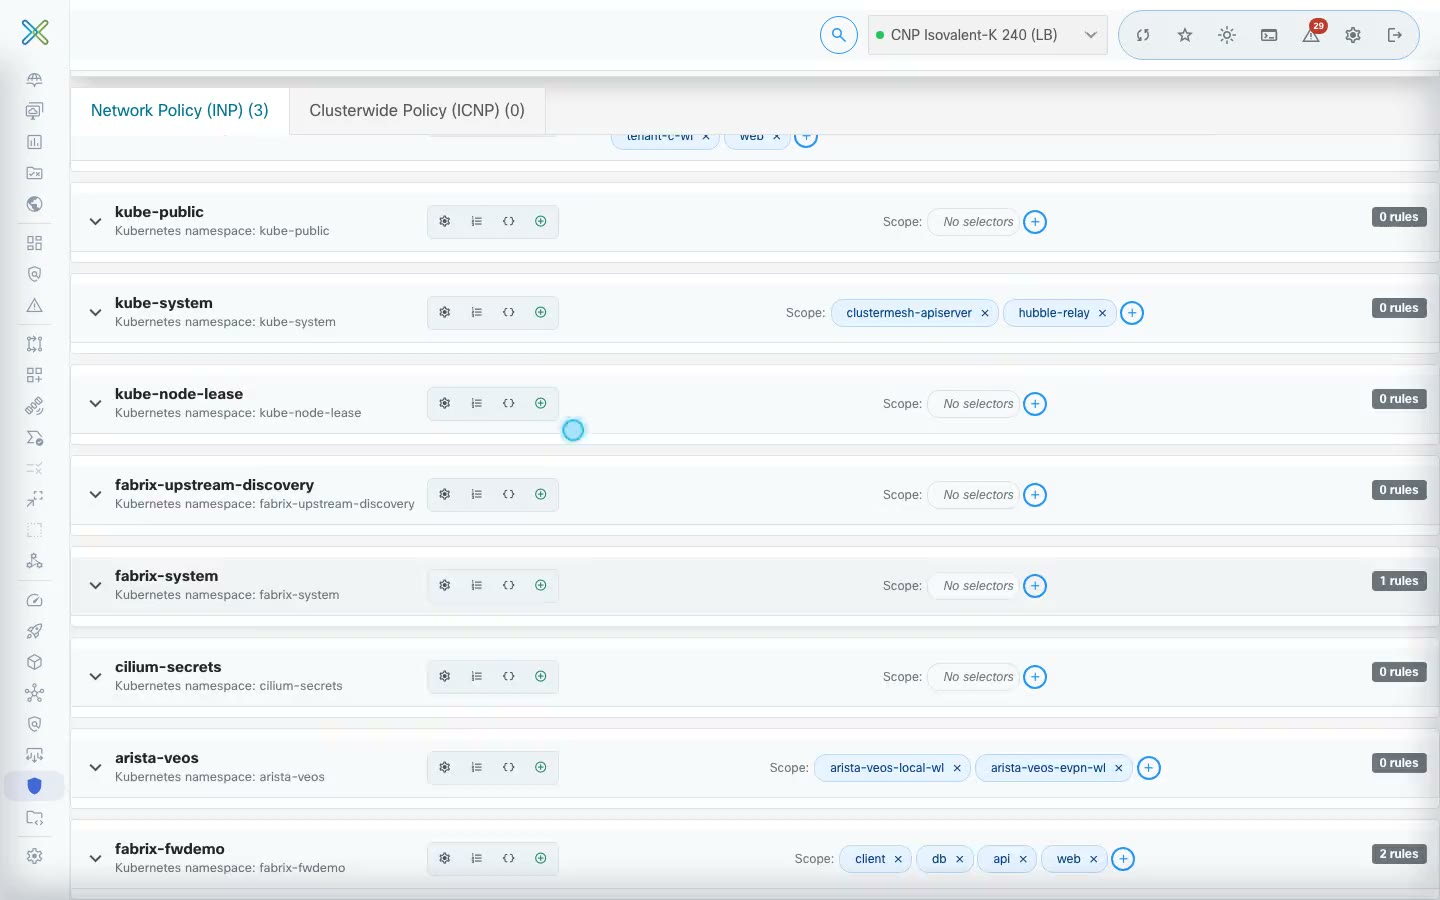
Firewall PoliciesThe firewall rule table, over a Kubernetes cluster.Rule table: source / destination / service / actionHit Count & RisksPublish Validation → Impact Analysis → PublishCluster baseline protection
For youLocal
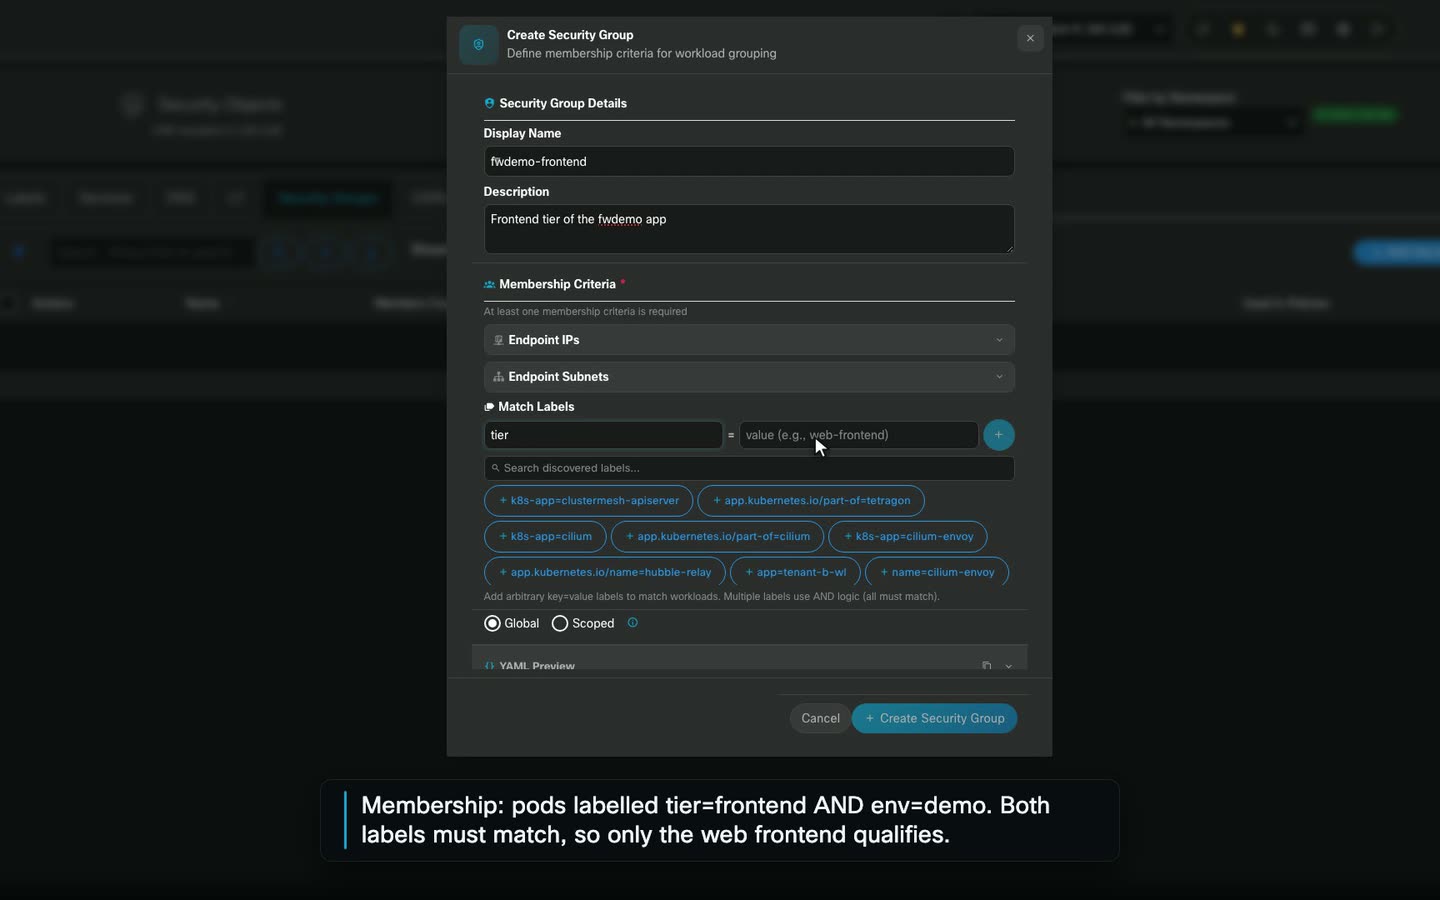
Security ObjectsThe building blocks: labels, services, groups, CIDRs, FQDNs.Labels · Services · DNS · L7Security Groups · CIDRsFQDN Groups · External Endpoints
For youUniversal
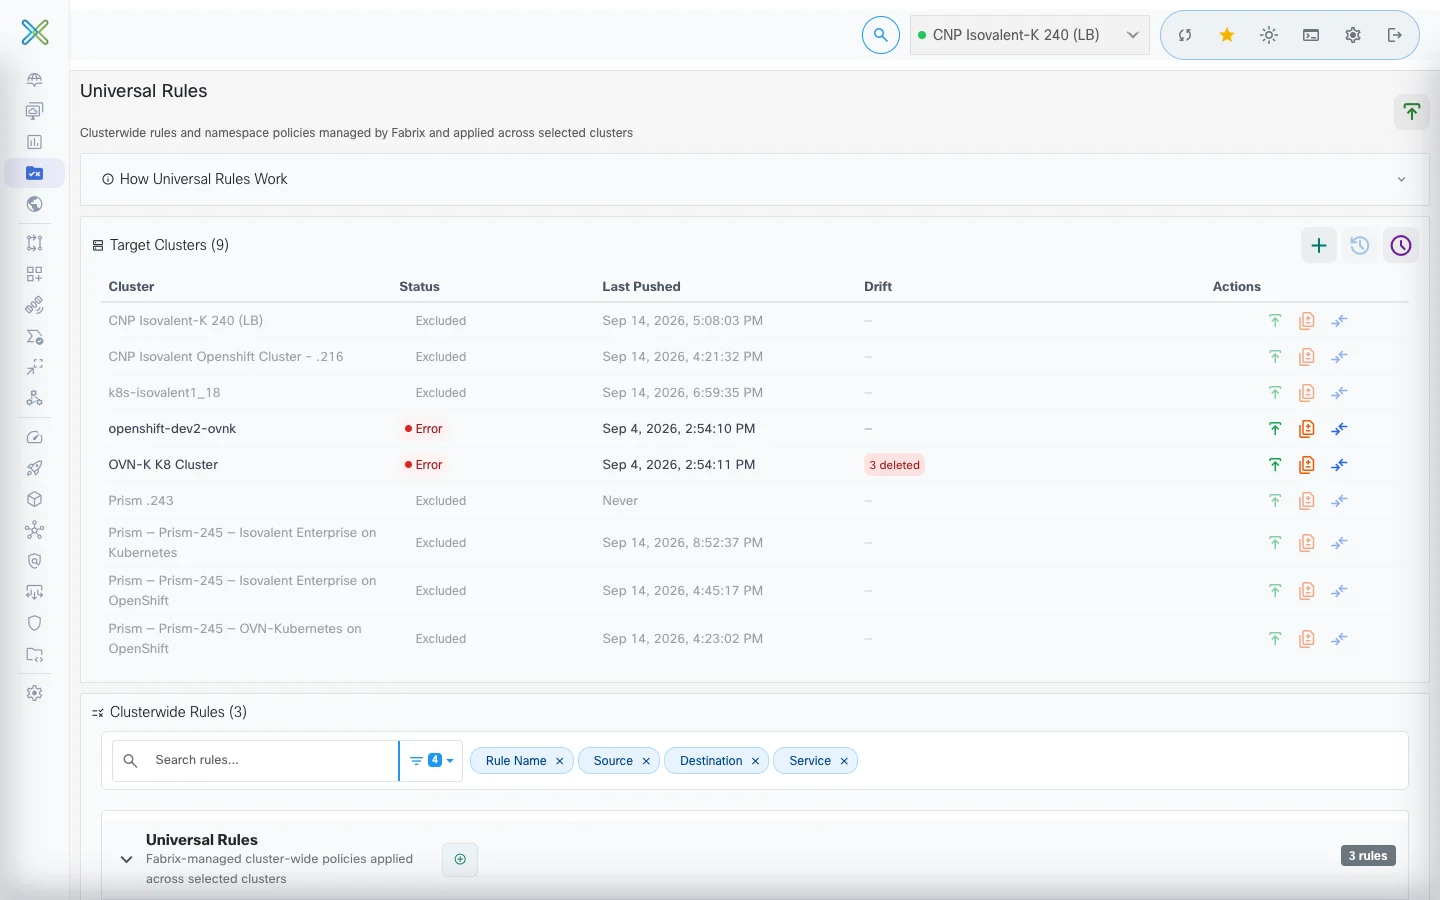
Universal RulesWrite once, publish to every cluster.Target clusters pickerPublish preview per clusterCheck Drift
For youUniversal
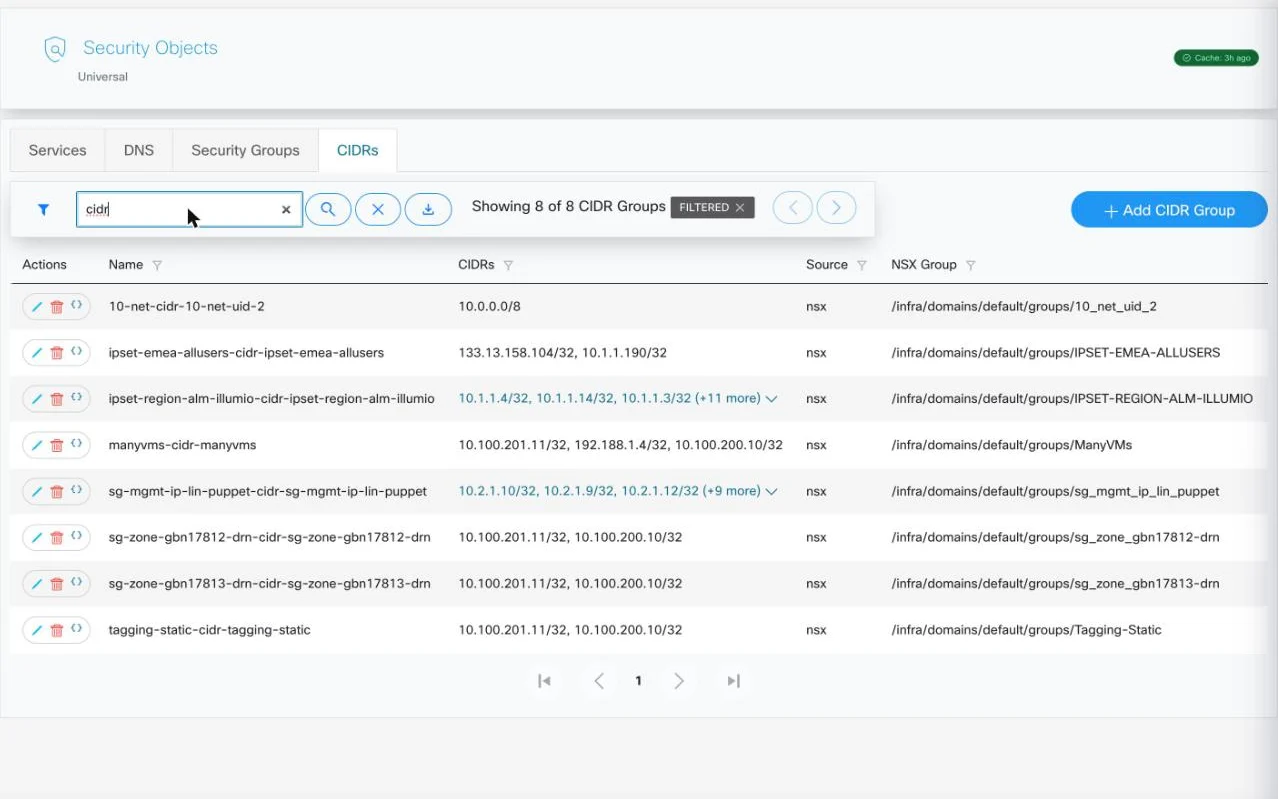
Universal ObjectsShared objects defined once and reused across clusters.Define once, reuse across clustersCilium-family datasources
For youOff-menu
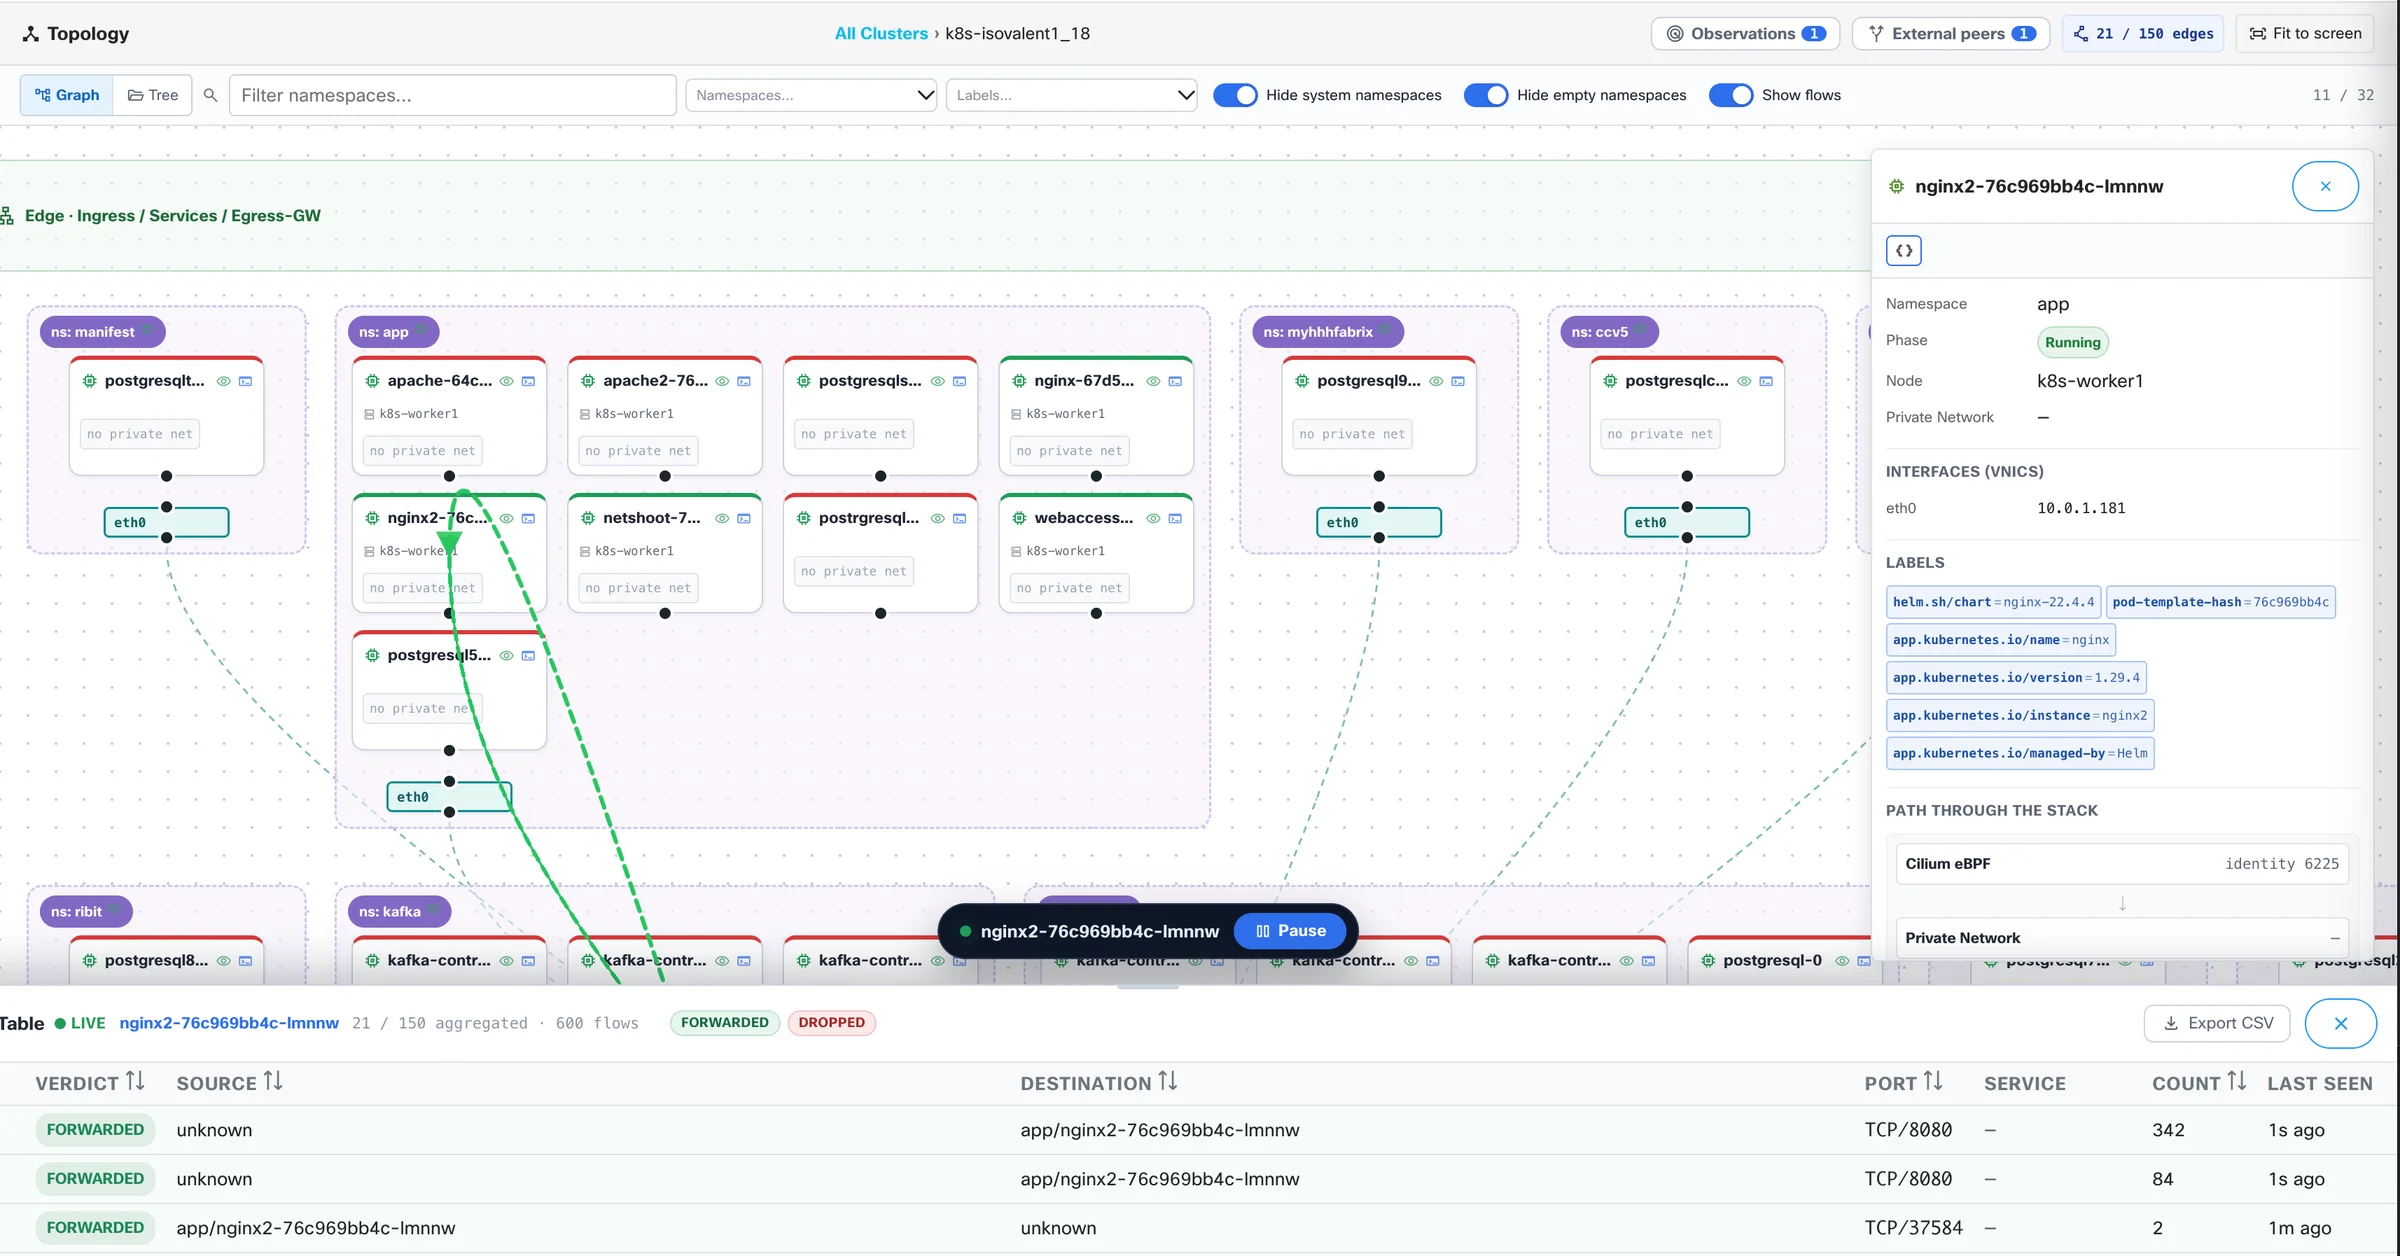
TopologyLive map of every workload, with Hubble flows on the edges.Live flows: forwarded / droppedCreate Allow/Deny policy prefilled from this flowStack layers down to the Physical Underlay
For youTools
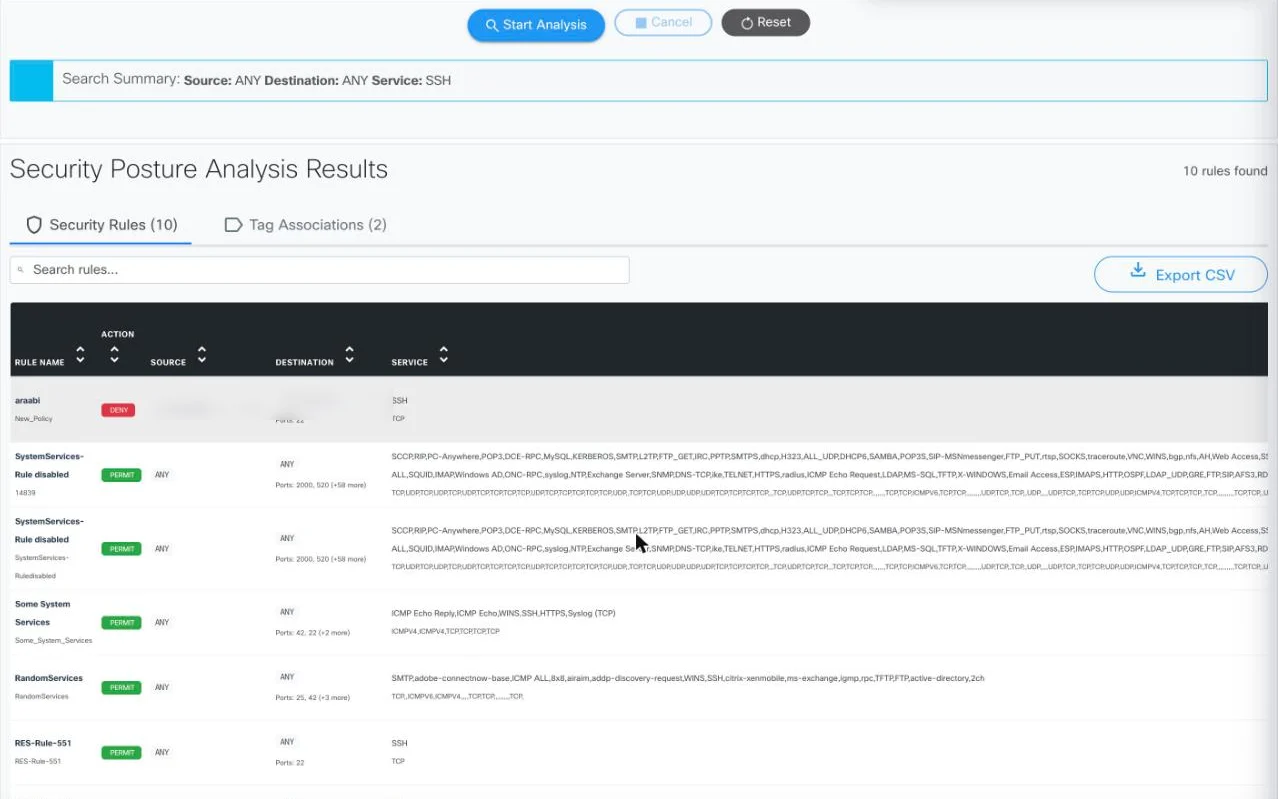
LocatorWhich rules affect this traffic?Search by workload, IP, tag, groupSource + destination rules
For youLocal
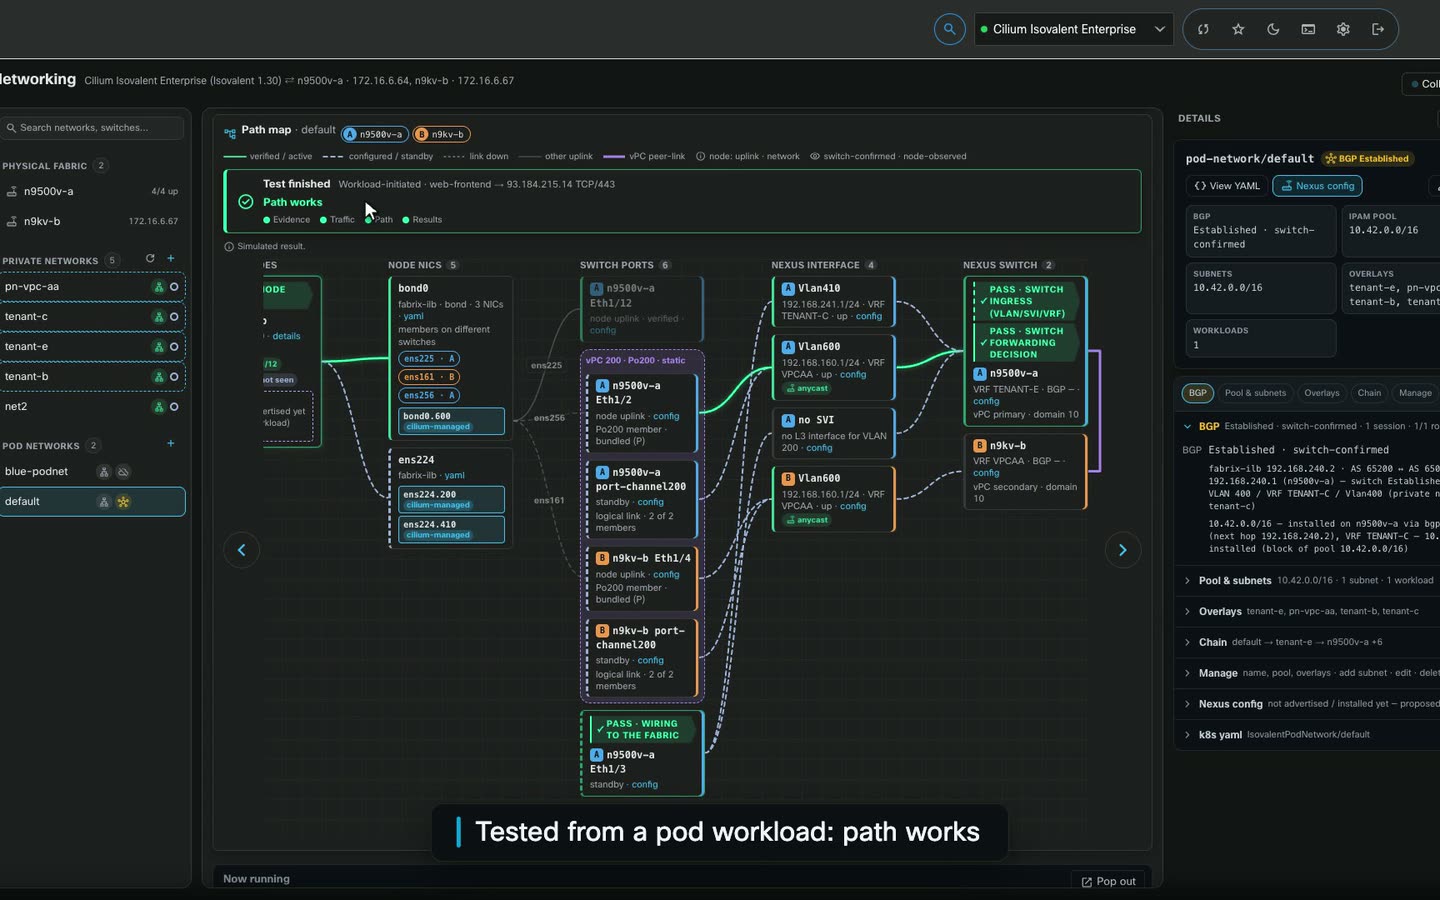
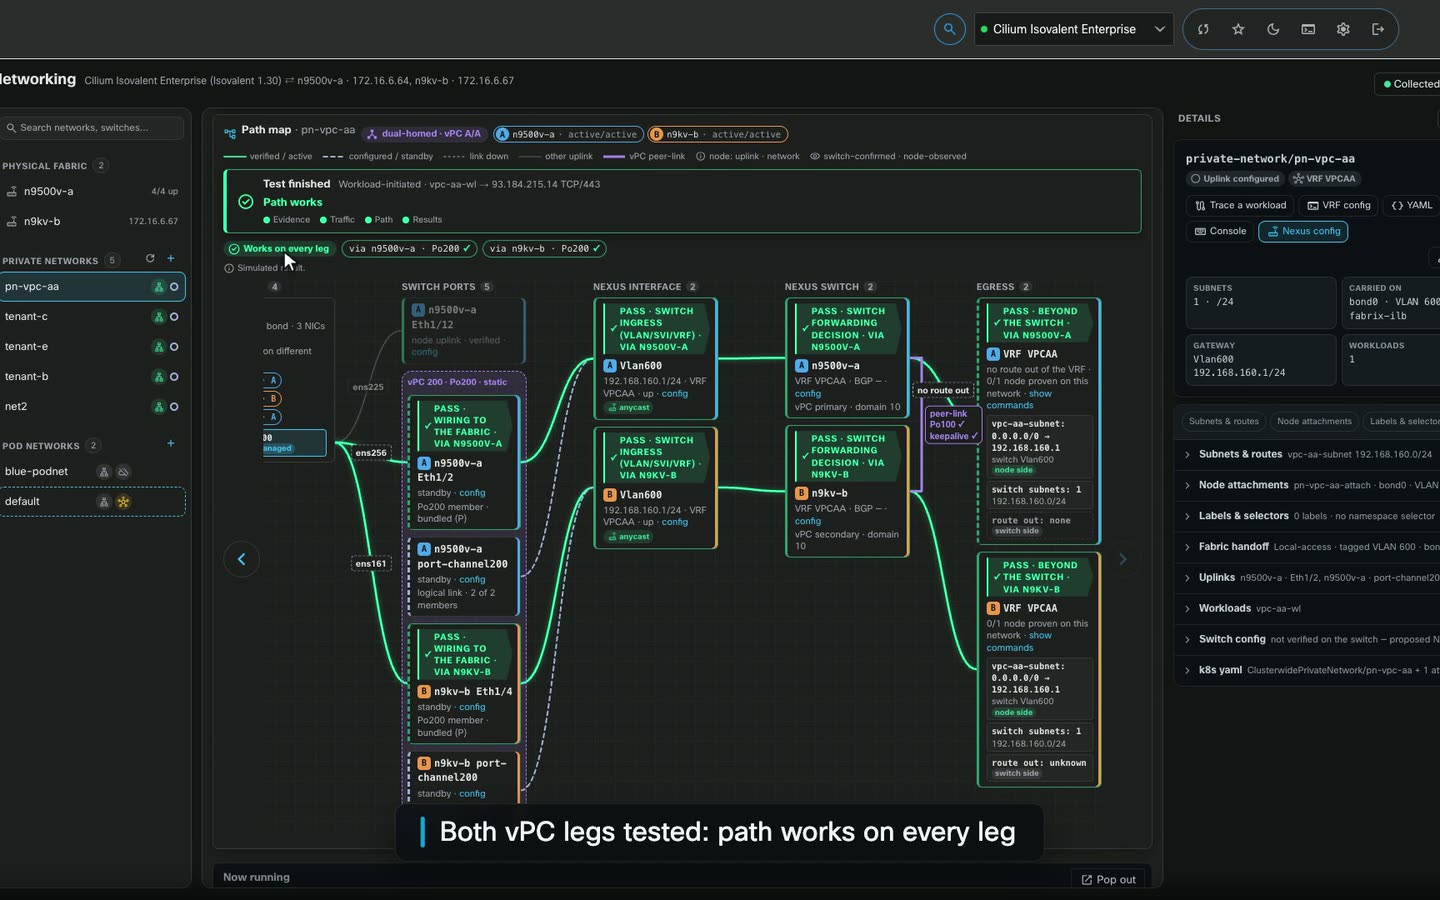
NetworkingPhysical + overlay networking, authored and traced.New Private Network (VLAN handoff or BGP EVPN)Trace path: workload → node → NIC → switch portFaceplate · Port LED · Interface statisticsPropose switch config (diff + revert)
For youOff-menu
Network TestProve connectivity hop by hop.Observe / probe / AnalysisTCP · UDP · ICMPEvidence per hop
For youLocal
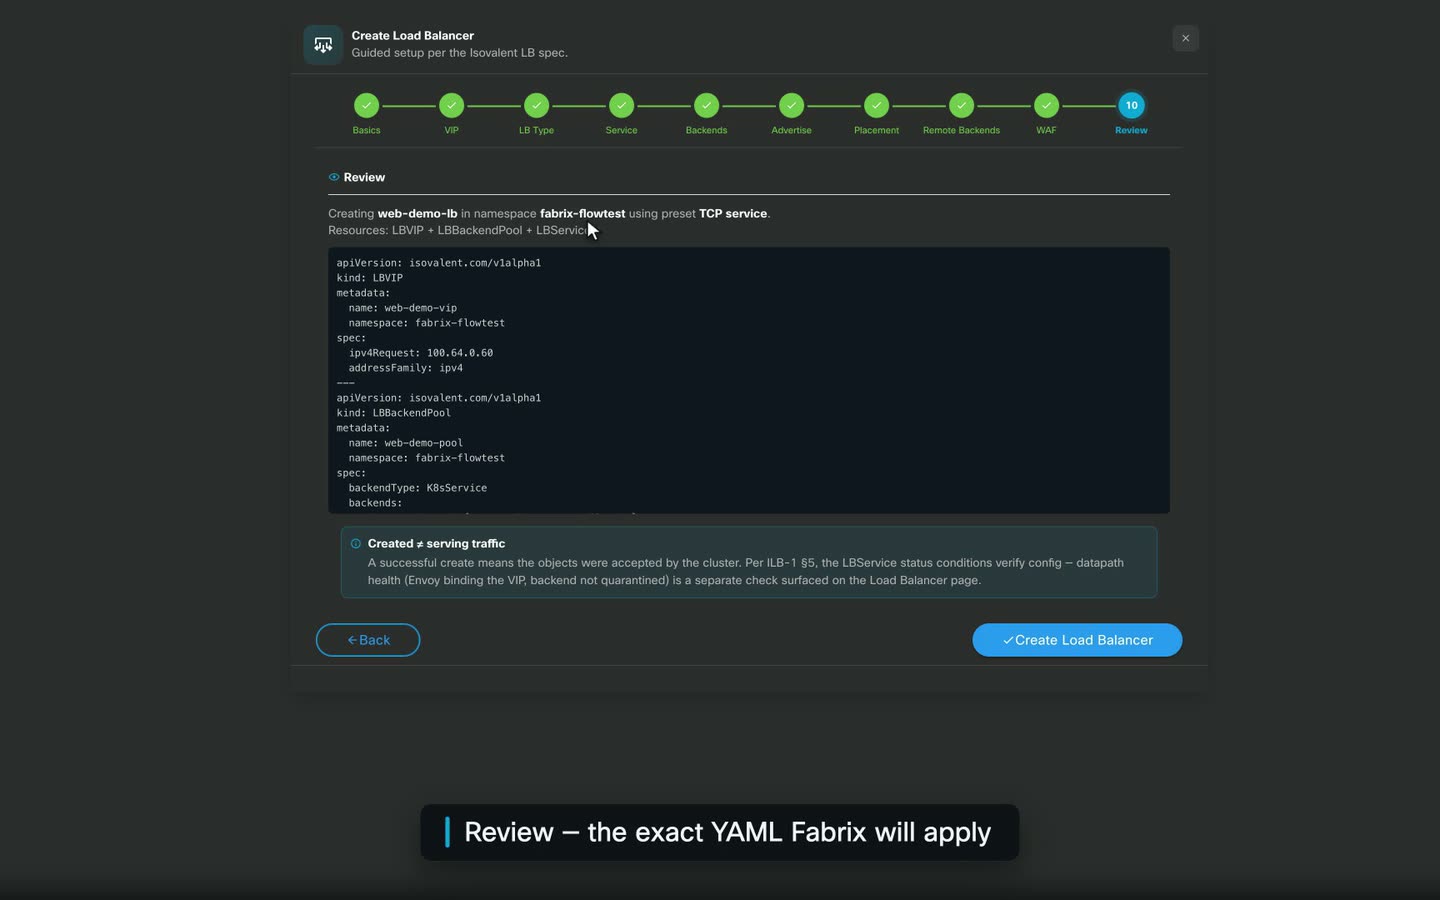
Load BalancerIsovalent load balancing with a live flow canvas.VIPs and poolsLive flow canvasBGP advertisement
For youLocal
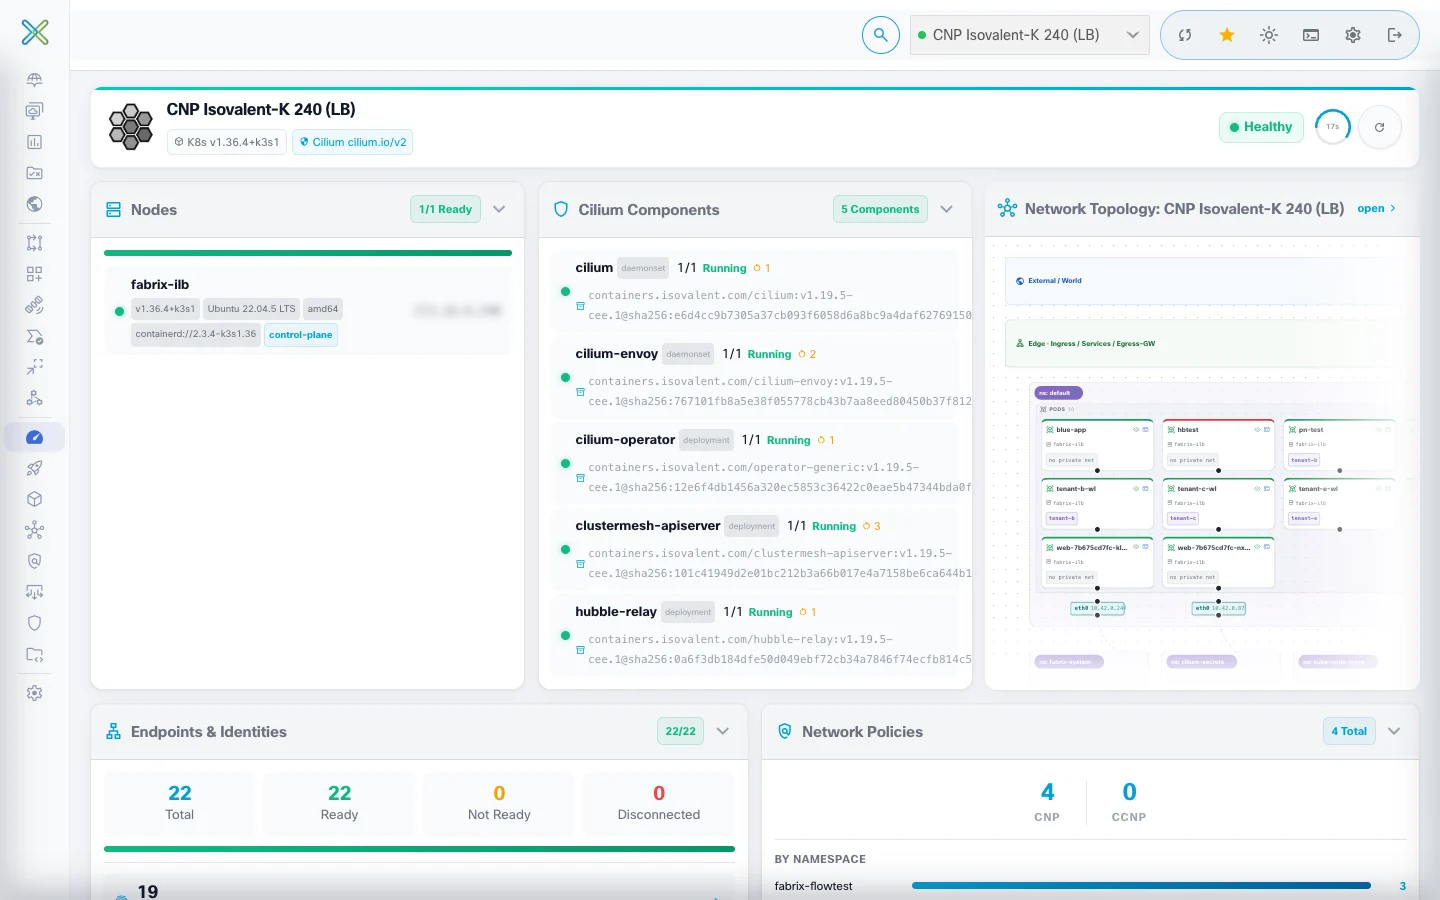
Cluster DashboardSingle-cluster health at a glance.NodesCilium ComponentsEndpoints & IdentitiesDiscovered CRDs
For youOff-menu
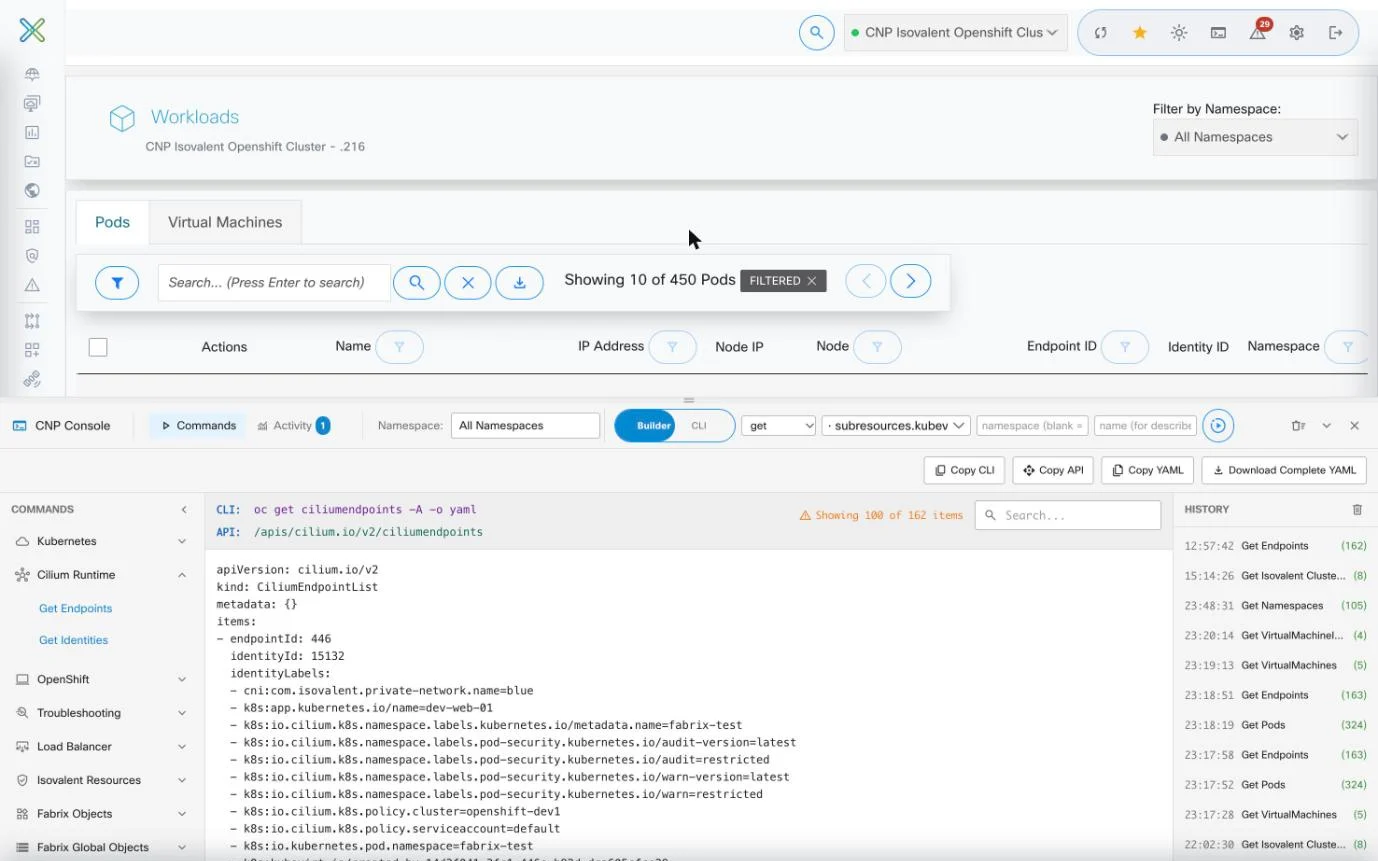
CNP ConsoleThe cluster, from a drawer: commands, YAML, and the API behind each click.Commands catalogue (Builder / CLI)API tab: captures the calls behind every clickEdit YAML → save to the clusterCopy kubectl command
For youLocal
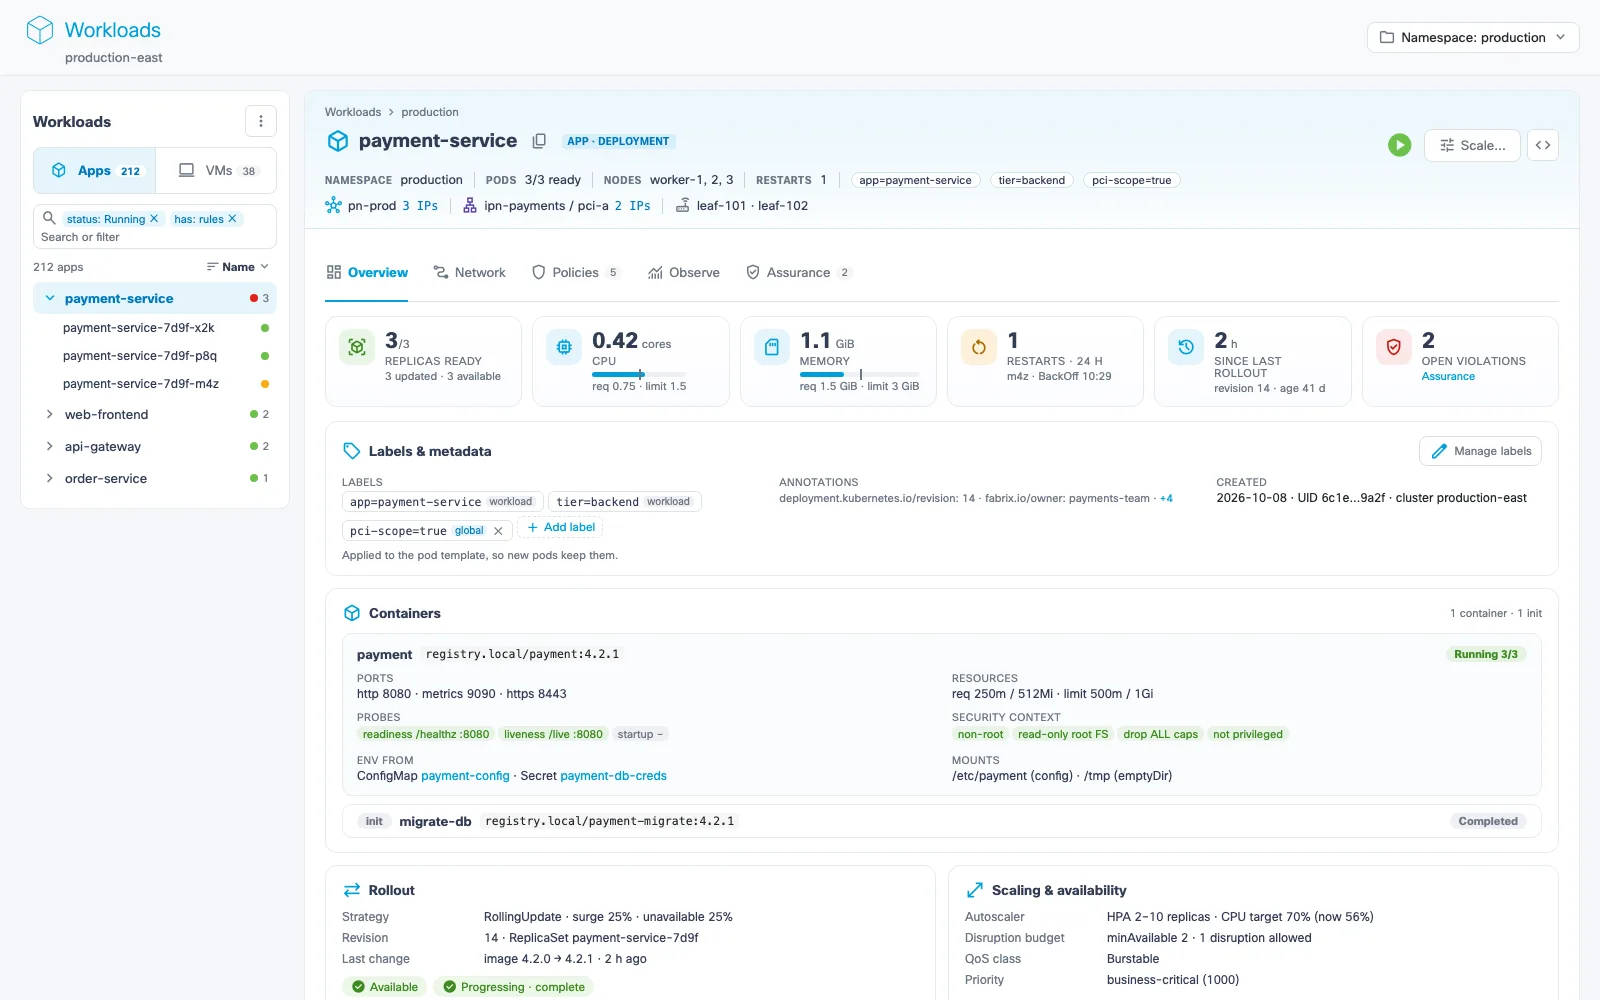
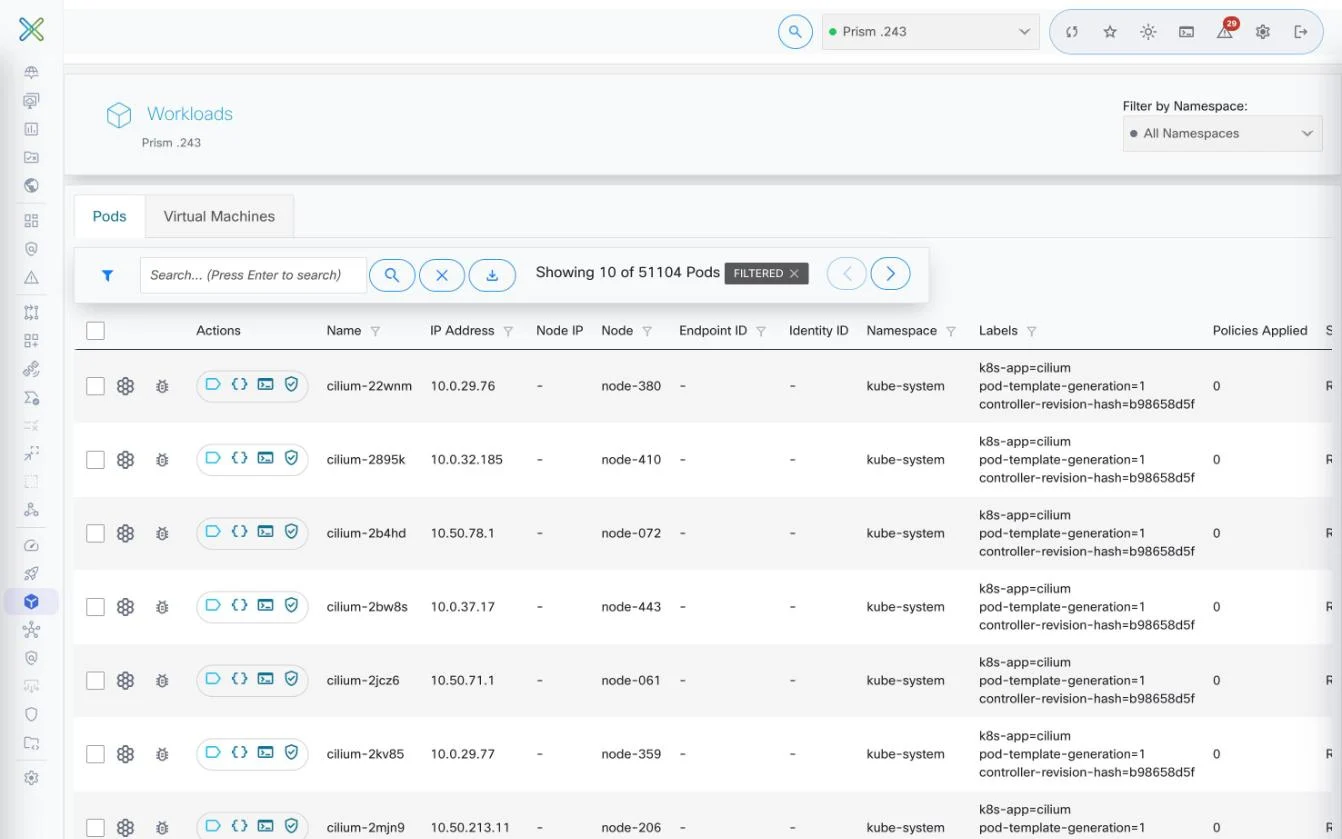
WorkloadsPods and VMs, with consoles and deep connectivity detail.Open Console · Debug commands · Endpoint InspectorVirtual Machines tab + serial consoleConnectivity: Effective Policy · Exposure · DependenciesTetragon: Recent processes · Privilege events
For youUniversal
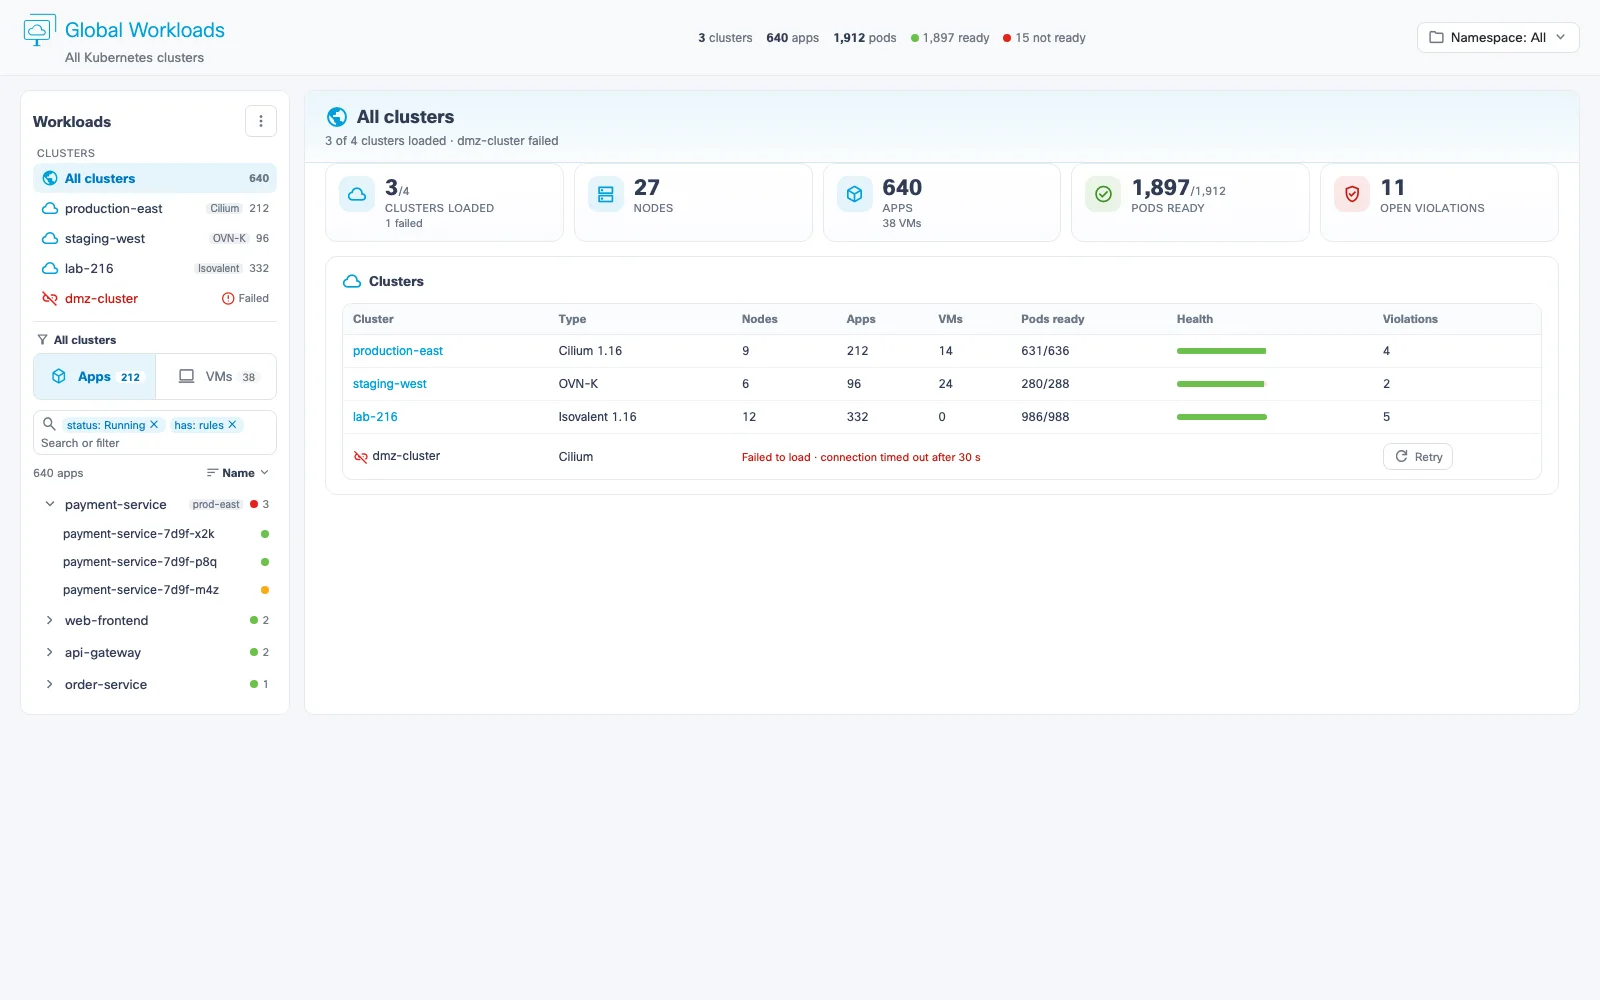
Global WorkloadsEvery cluster, namespace, pod and VM in one tree.Cluster → namespace → pod / VM treeEndpoint detail: usage, policies, activity
For youLocal
Repo BrowserGit mode: policy as code.Git mode for GitOpsBrowse published policy in Git
Screenshot · Repo Browser
For youLocal
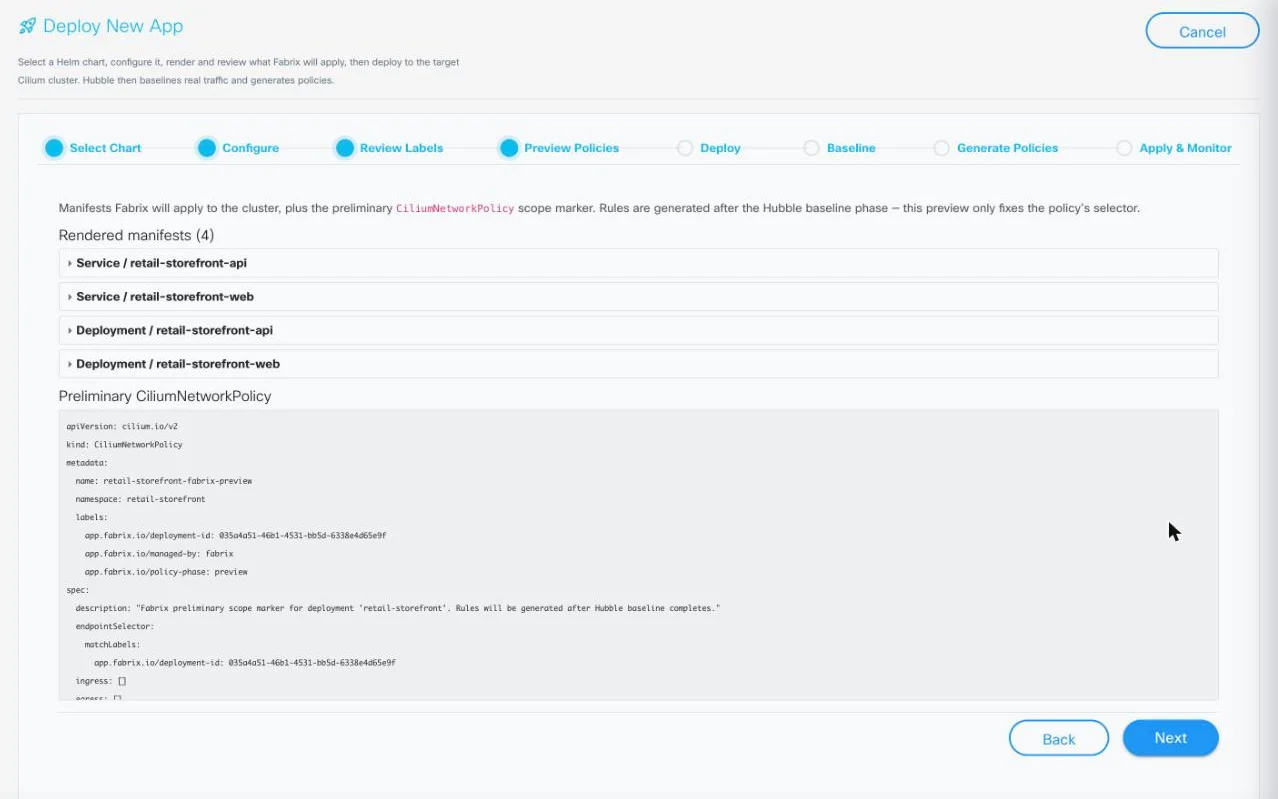
AppsDeploy an app and secure it from its own traffic.Deploy New App (Helm chart)Baseline → Generate Policies → Apply & MonitorSecure Existing App
For youTools
CanvasDesign app policy visually; YAML writes itself.Model app tiers, ports, L7Live CNP YAML
For youTools
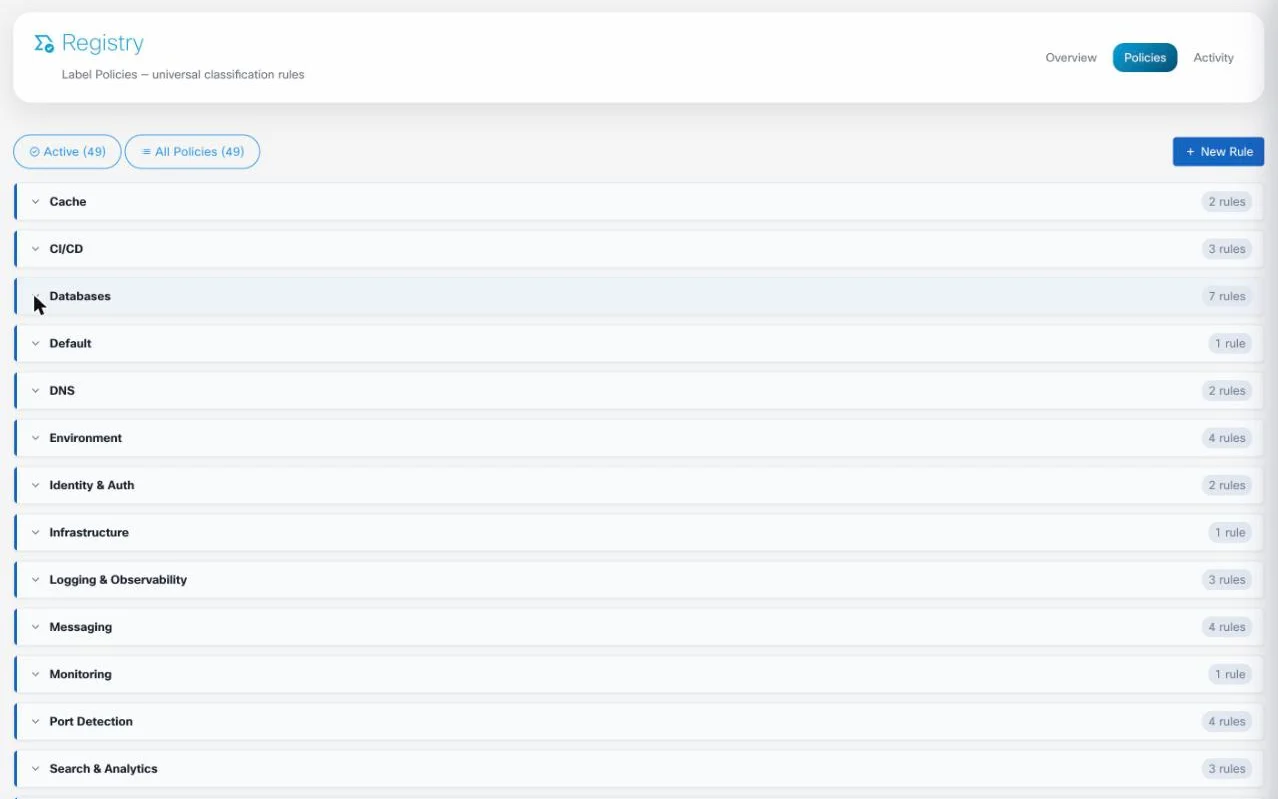
RegistryEnterprise workload label management.Compliant / Mismatch / MissingAudit · Suggest · Enforce
For youTools
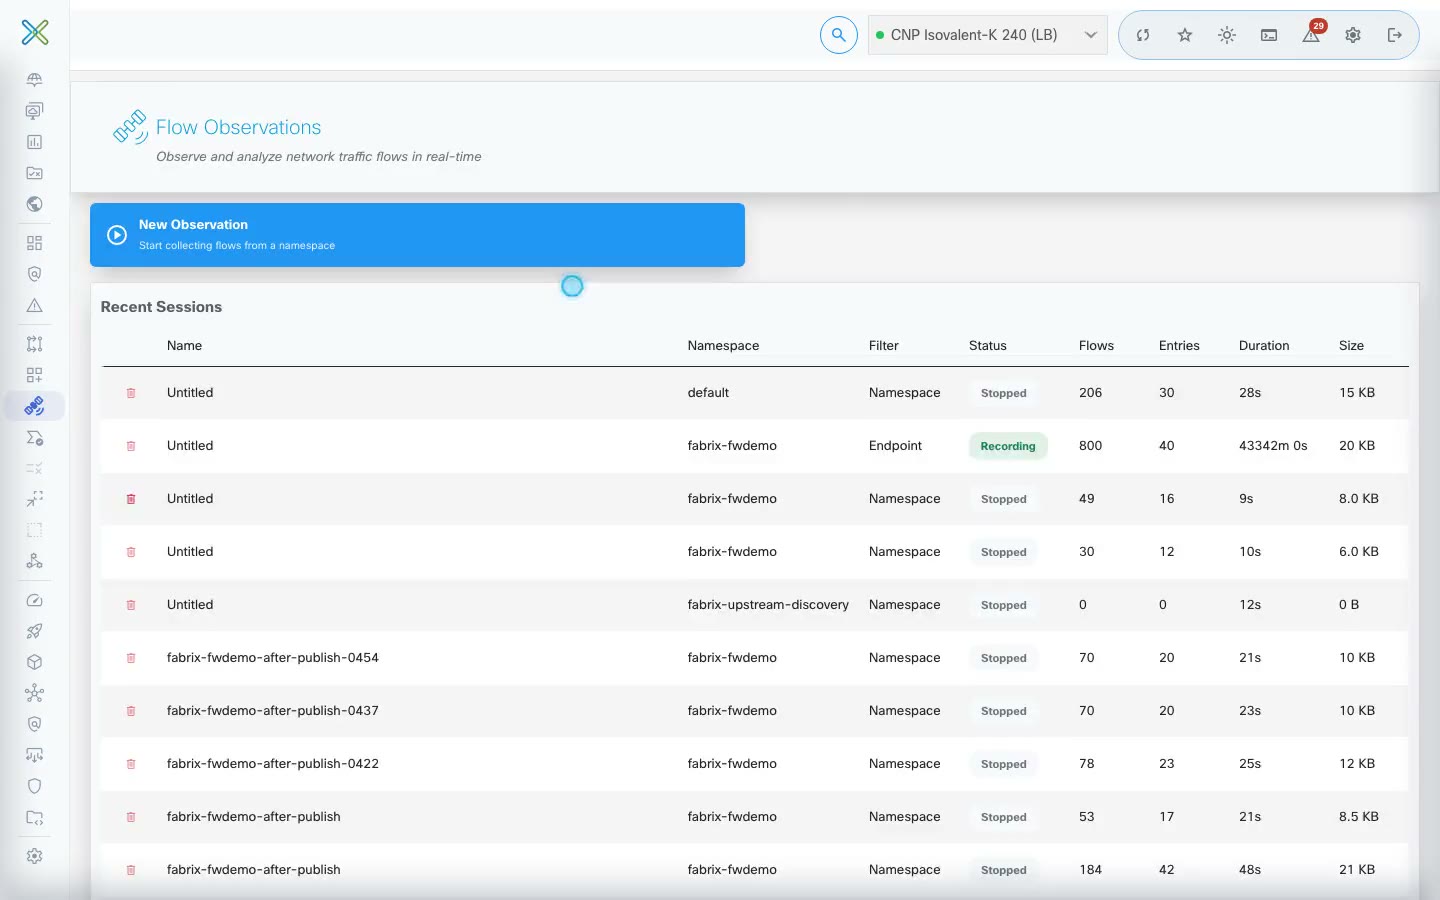
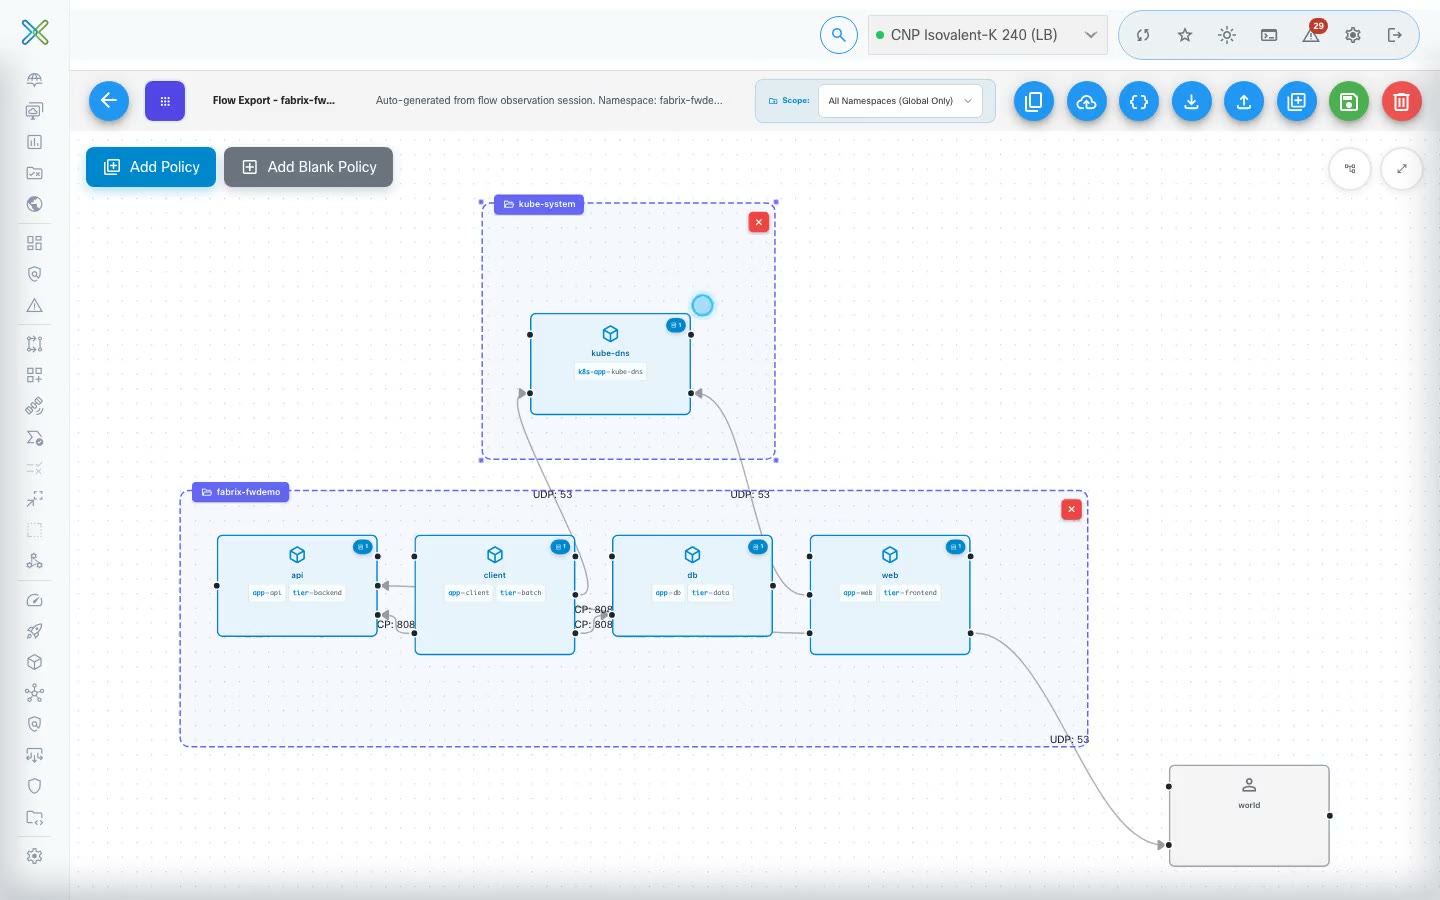
ObservatoryRecord flows, find the gaps, export the policy.Record the app's trafficPolicy Gap AnalysisAlert rulesExport to Canvas
For youAssurance
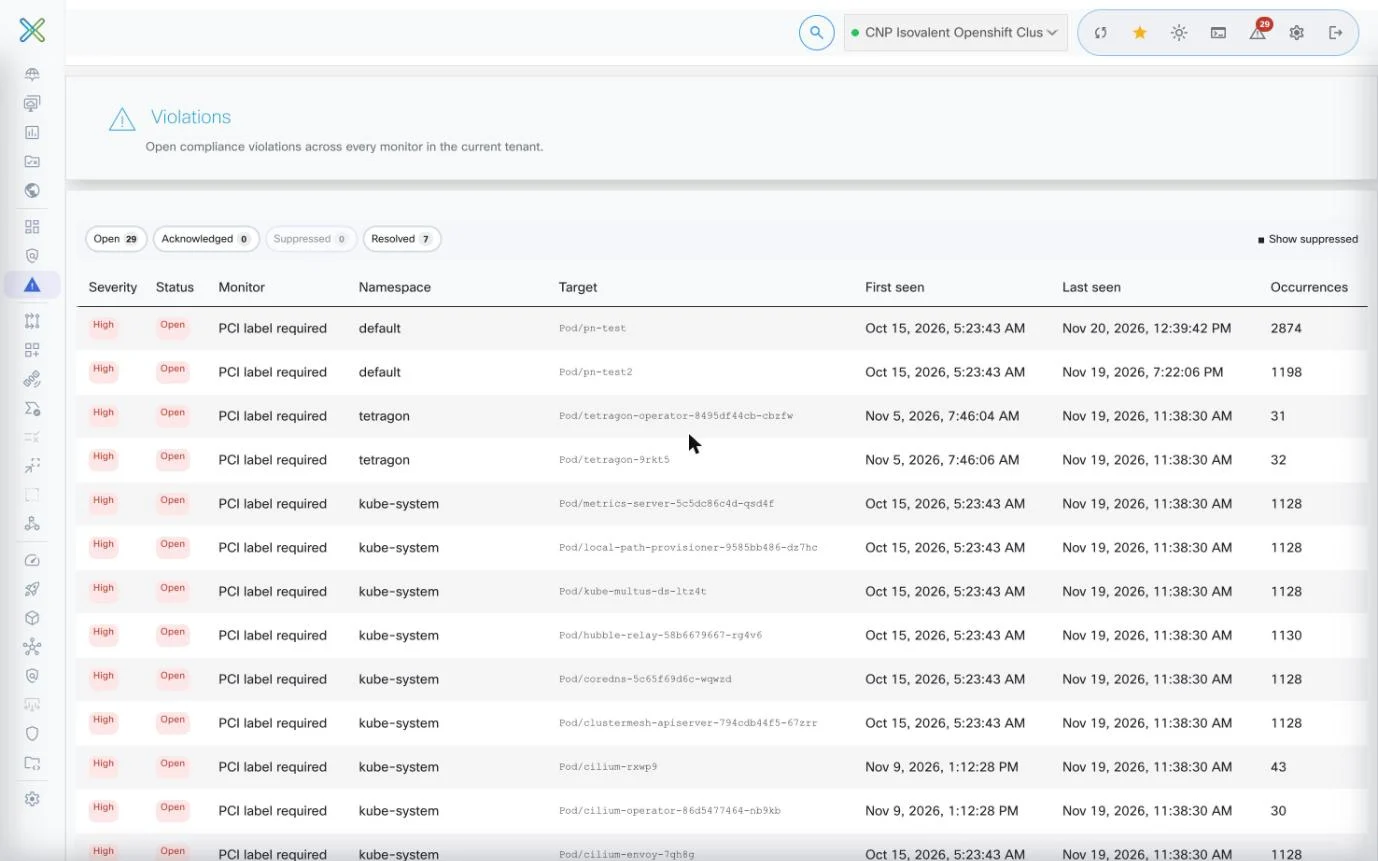
AssuranceContinuous checks on how workloads should look and behave.Dashboard: open violations by severityMonitors: Baseline from workloadRuntime Monitor (Tetragon allowed processes)Violations: Acknowledge / Suppress / Reopen
For youUniversal
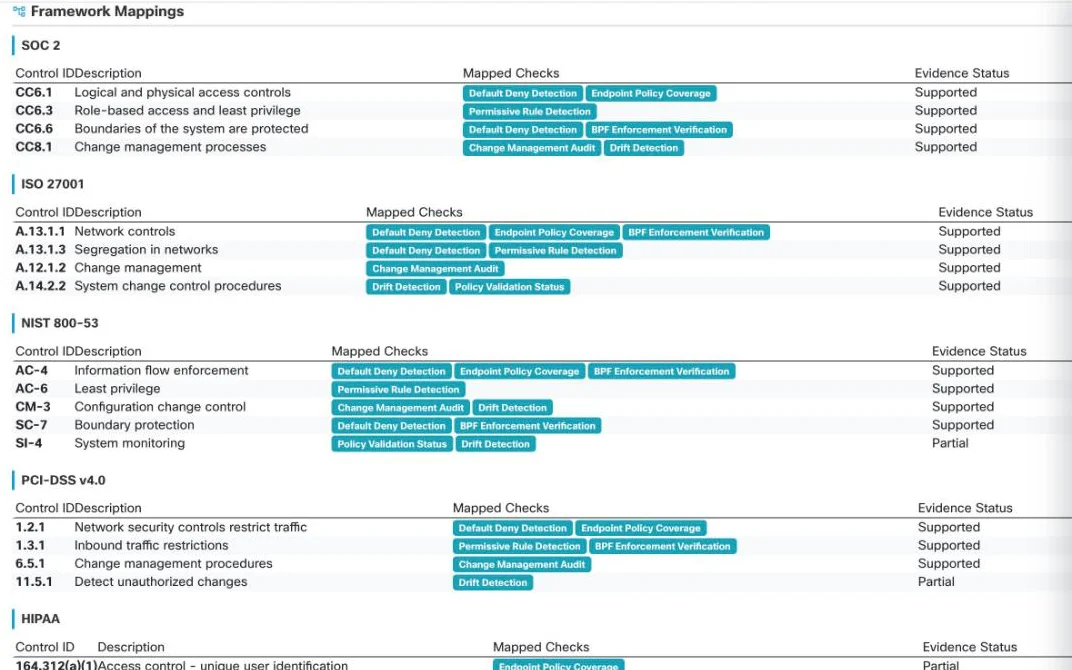
Compliance ReportsAudit-ready posture, mapped to frameworks.Executive Summary scoreFramework MappingsEnforcement Evidence · Drift AnalysisPDF · Excel · JSON export
For youUniversal
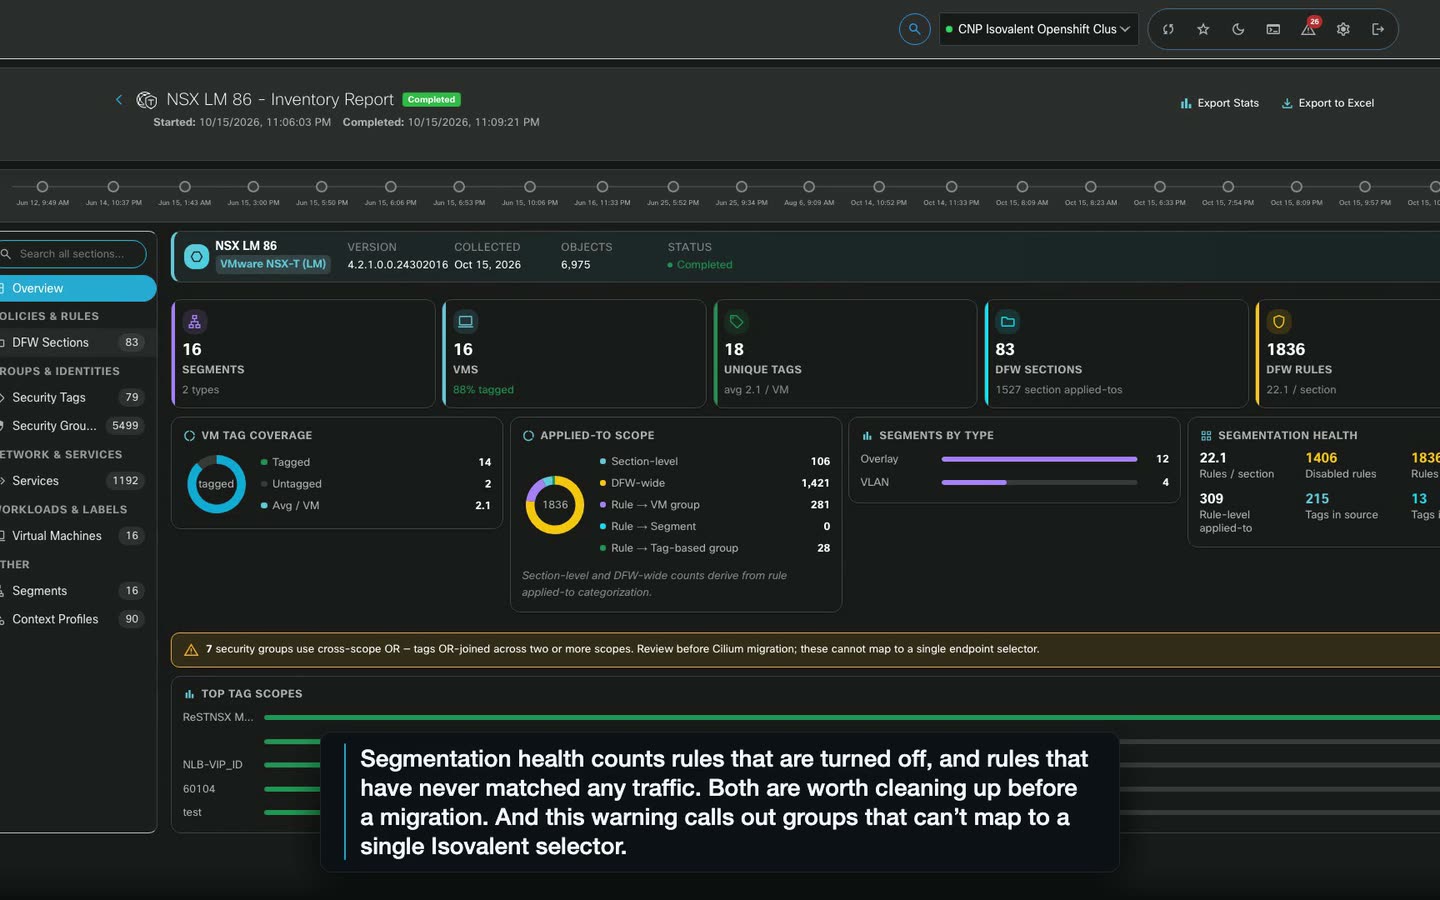
Inventory ReportsThe As-Is baseline for every source.As-Is baselineNSX · FMC/FTD · ASA · ISE · vCenter · Check PointExport to Excel
For youUniversal
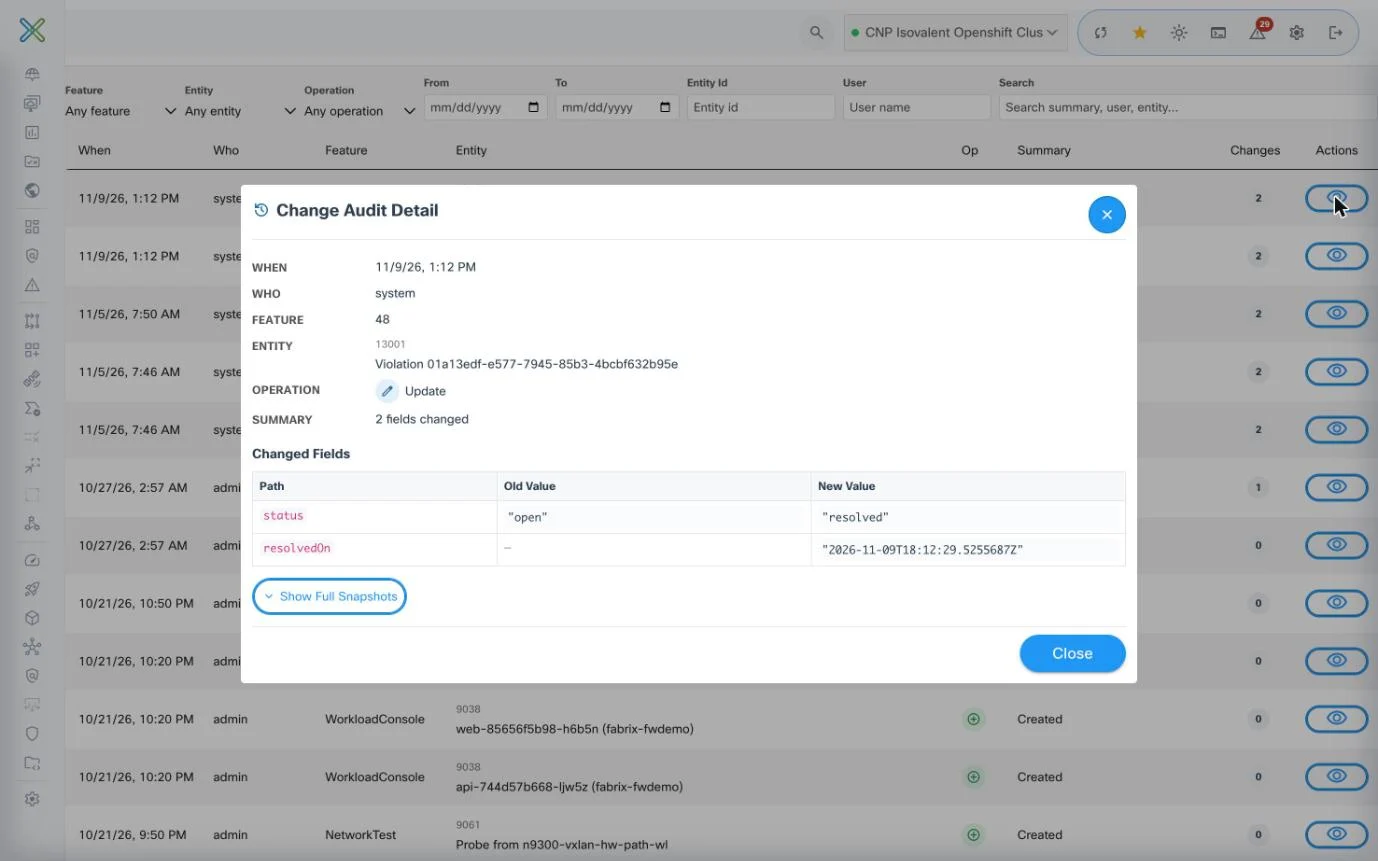
Change AuditOld vs new object for every change.Old vs new objectFilter by feature, user, operation
For youTools
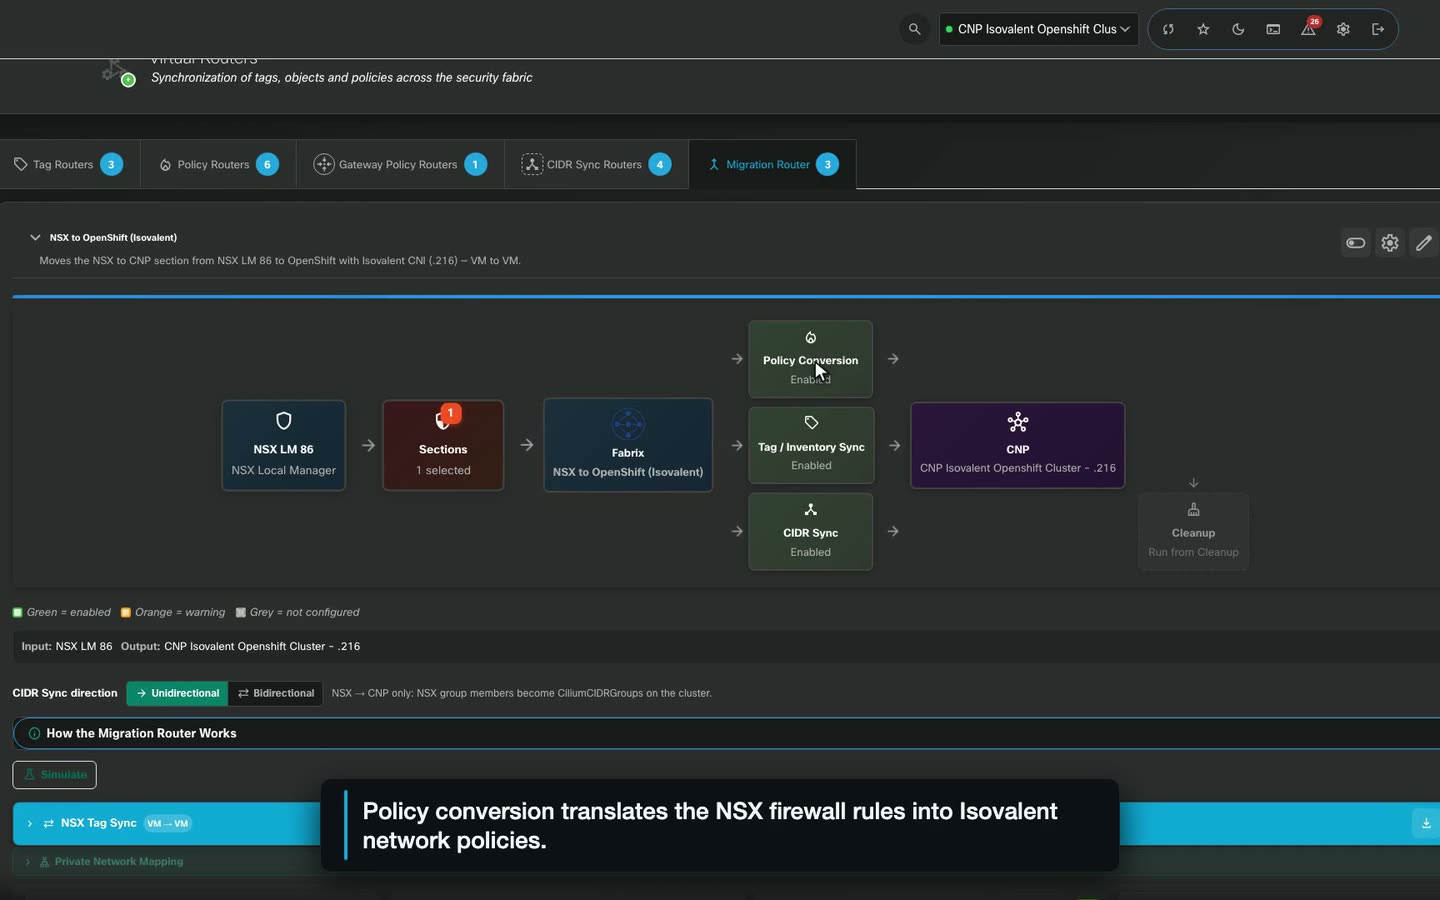
vRouterNSX to Cilium in one pipeline, simulated first.Migration Router: Simulate → PublishTag RoutersWhat-If Scenario RunnerMigration Wave Planning · Rollback Sync
For youTools
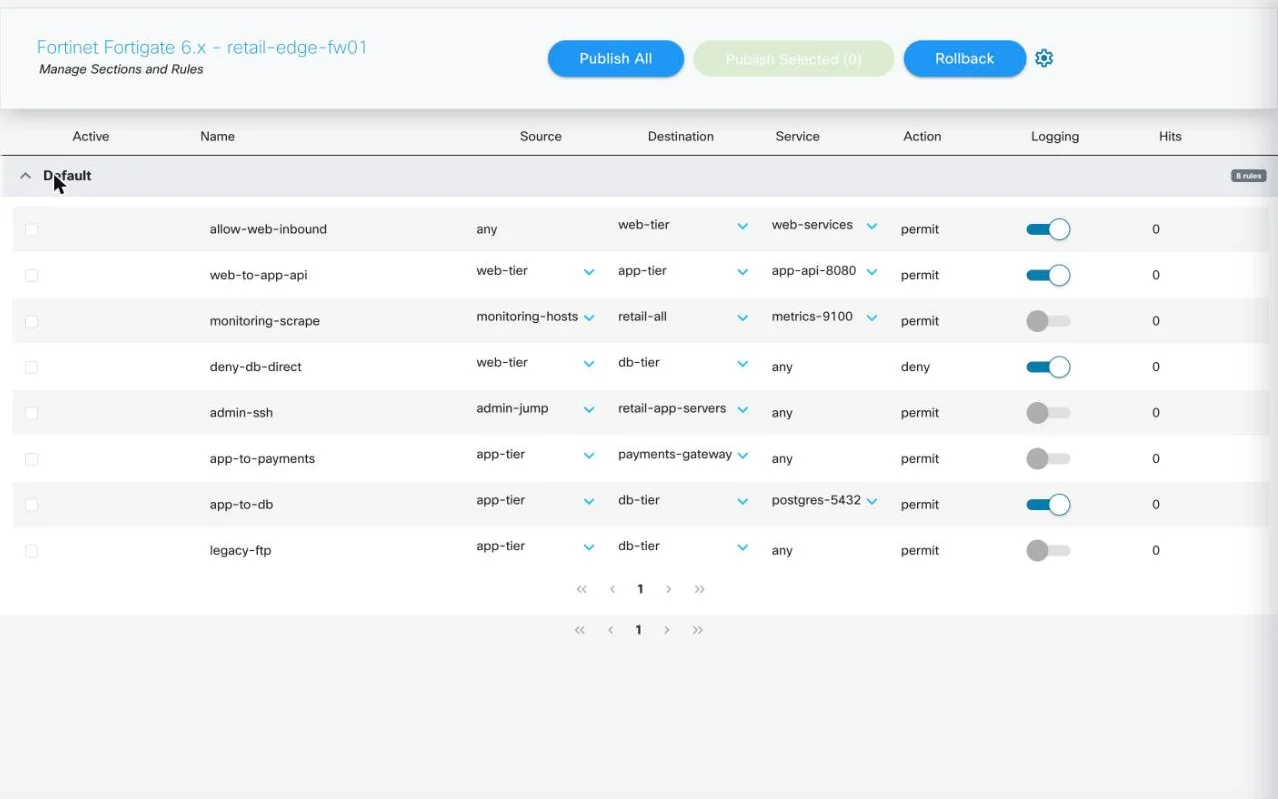
TransformerConvert firewall configs to Cilium policy.Palo Alto · Check Point · Fortinet · ASA/FTDPublish as CNPRollback
For youTools
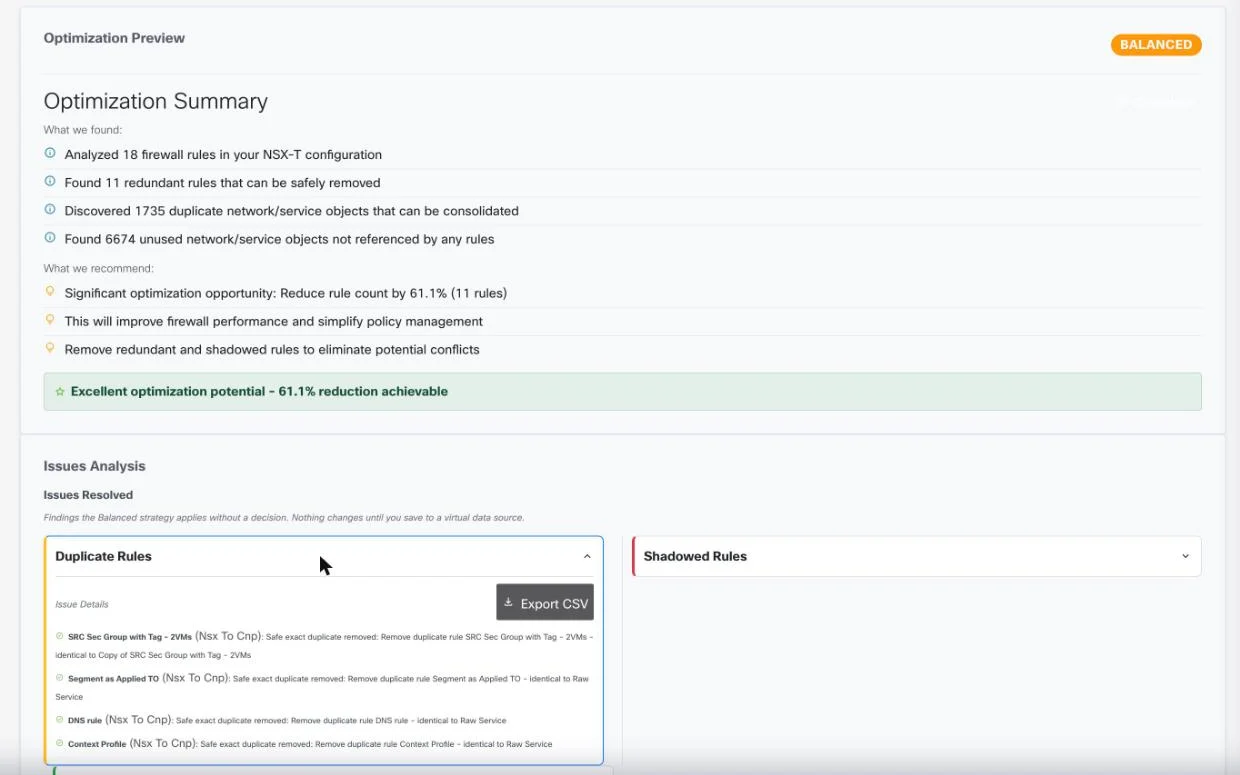
RefineryClean the rule base before you move it.Conservative / Balanced / AggressiveUnused Objects Analysis
For youTools
ComposerCompose firewall policy for non-Kubernetes datasources.Compose firewall policyNon-Kubernetes datasources
Screenshot · Composer
For youUniversal
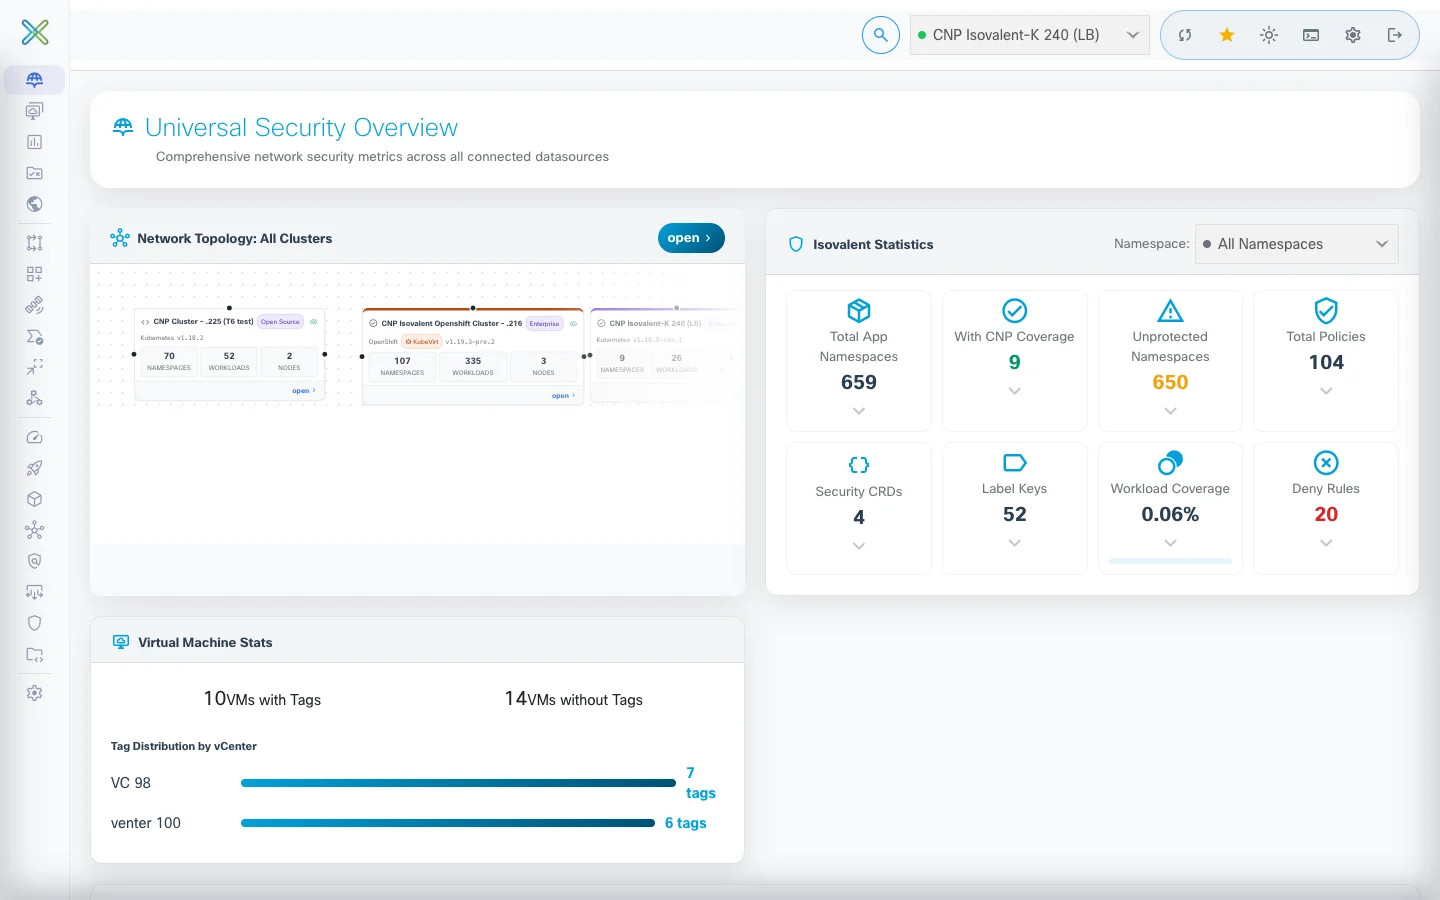
Universal DashboardCoverage across every datasource.Workload Coverage %Unprotected Namespaces
For youSystem
PrismA whole cluster estate on one node.Target-scale clusters on one nodeScale with a sliderRehearse a migration at scale
For youSystem
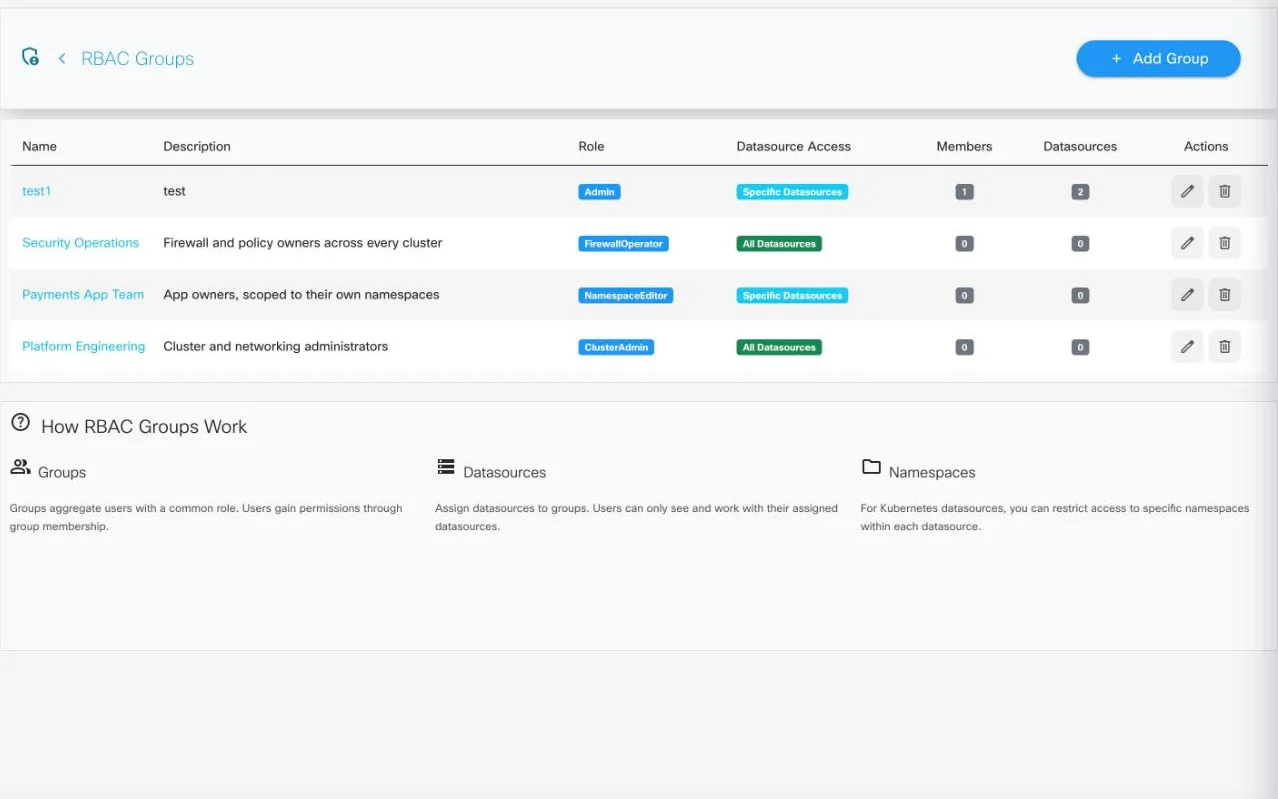
Access & deploymentEnterprise controls, fully self-hosted.RBAC GroupsLDAP / OIDC SSOAir-gapped, no call-homeSecret Rotation
 RESTNSX
 ISOVALENT
 OPENSHIFT