vRNI Flow Analyzer
The Security Planner turns flows into NSX policy in 3 steps.
 RESTNSX
CloudControlIntegrated Tools
Object and device-level, one-click troubleshooting. For example, run show edge <edge-id> nat through the Central CLI.
Run object and device-level tasks in one click.
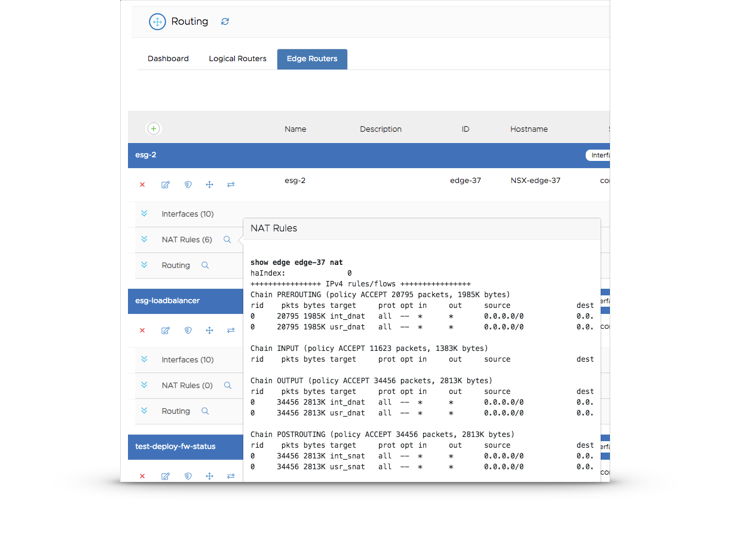
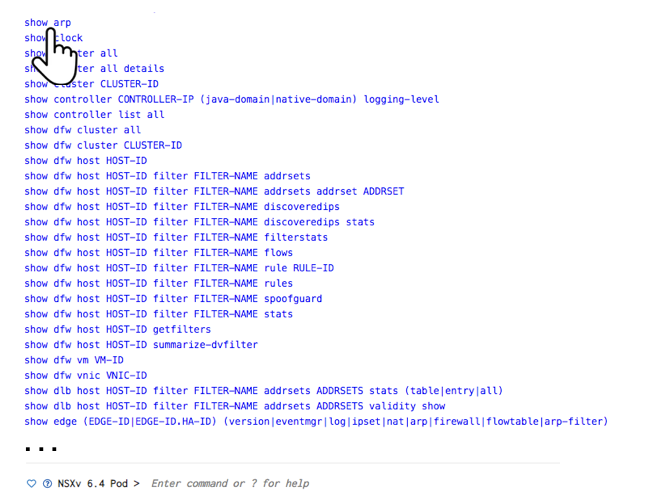
Run NSX CLI commands through the Central CLI.
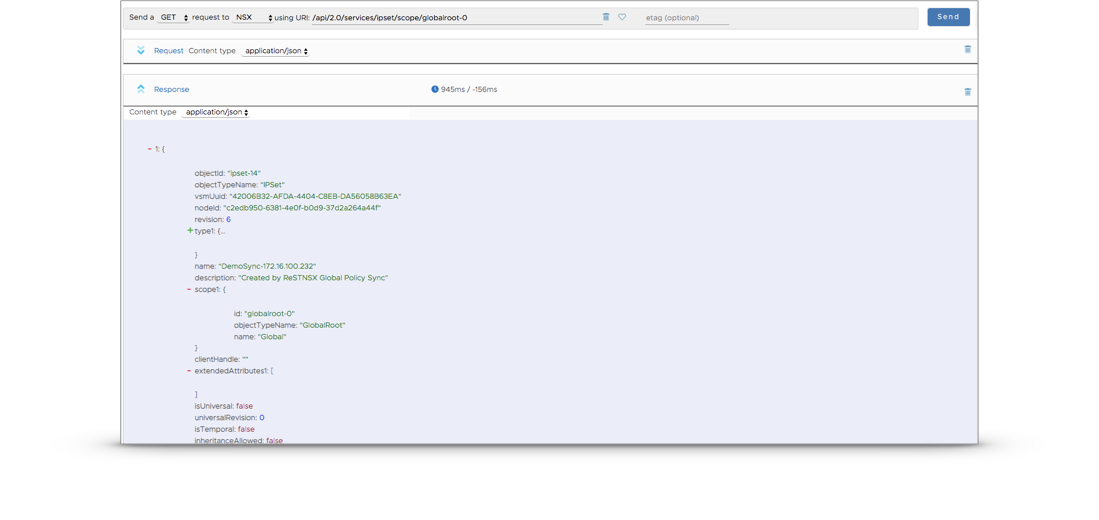
Run GET, POST and PUT calls without handling authentication or URIs, with favorites and history.
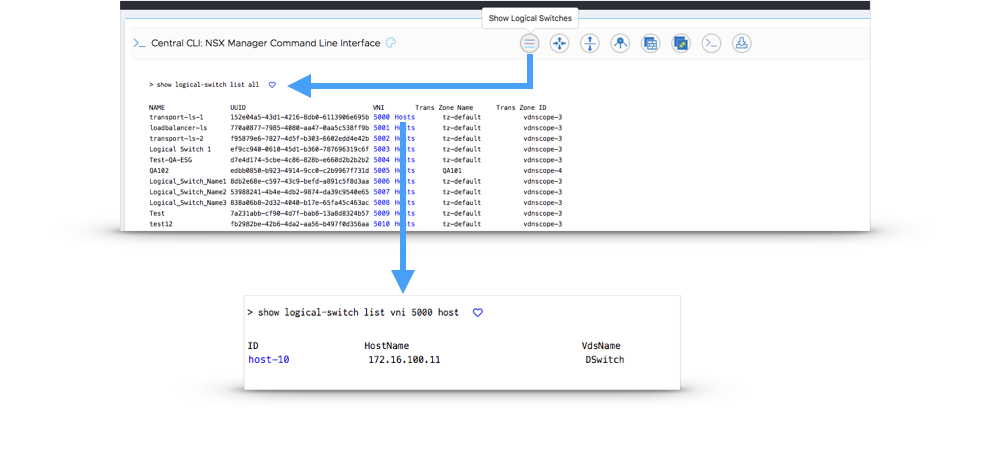
Intelligent hyperlinks for one-click troubleshooting.
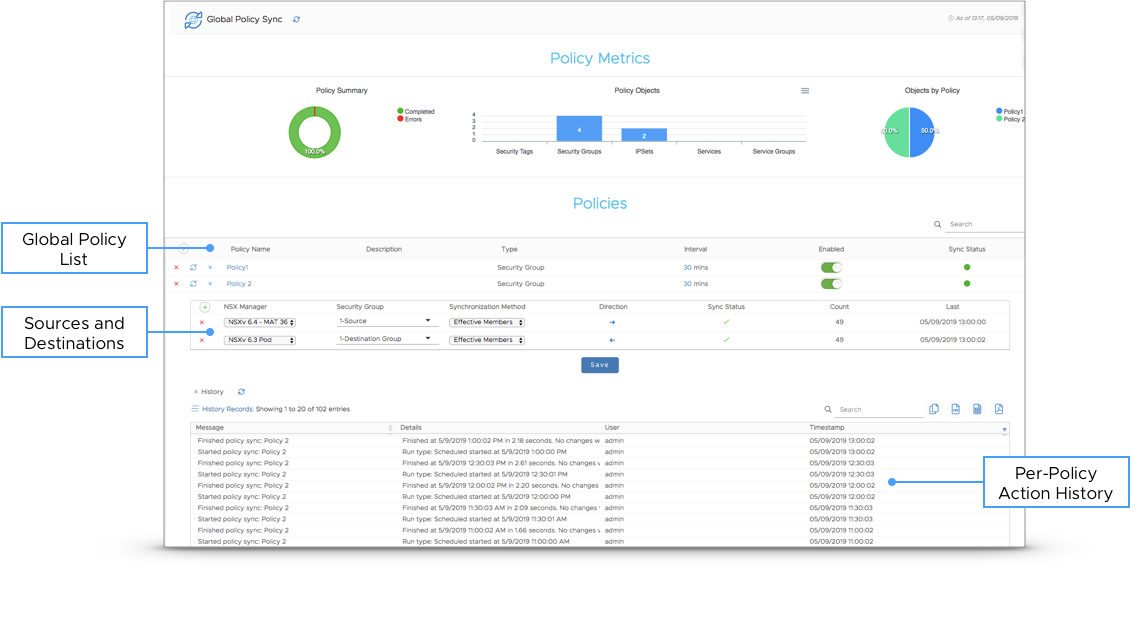
Synchronize NSX-v to NSX-v, NSX-T to NSX-T, and NSX-T to VMware public cloud, one time or ongoing, with a global policy view.
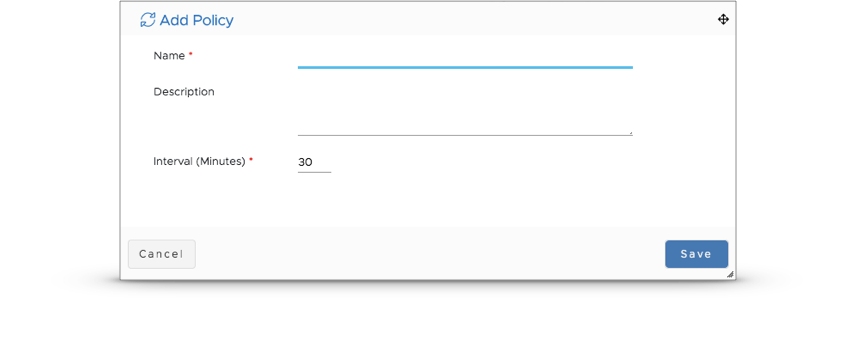
Create a policy with a name, a description and a synchronization interval in minutes.
The Security Planner turns flows into NSX policy in 3 steps.
Section and rule views, hit counts and Top N.
Firewall conversion through the Security Planner.
Check VM dependencies before a cloud move.
Rule migration with proprietary conversion scripts. We ingest Cisco, Juniper, Checkpoint and legacy NSX configurations.
Custom demo